
Samya Namdeo
Financial institutions need a reliable, portfolio-wide view of contractual exposure to manage risk with confidence. Contract intelligence connects agreements, obligations, controls, and regulatory requirements in one actionable framework. When an audit coincides with a vendor outage, teams can move decisively because the relevant terms, responsibilities, and response options are immediately accessible.
TL;DR
Contract data gives risk teams a clear view of duties, rights, limits, and exposure across business relationships.
Additionally, a lifecycle approach enables institutions to identify, assess, reduce, monitor, and report contractual risk.
Across large contract portfolios, AI can extract key terms, compare clauses, summarize obligations, and flag policy gaps.
Effective controls depend on clean data and clear ownership, supported by workflows that are useful and access rules tailored to each business unit.
By linking decisions, approvals, obligations, and evidence in a single trusted record, contract intelligence supports audits.
With alerts, workflows, reviews, and performance reports, CLM software turns contract insights into action in daily operations.
What Is Contract Intelligence in Financial Services?
Contract intelligence uses software to find, organize, and explain useful information in agreements. It can identify parties, dates, fees, service levels, renewal terms, liability limits, and duties. The software can compare language against company policies and approved clauses.
Financial institutions manage several types of contracts. These include vendor agreements, loan documents, custody agreements, broker arrangements, technology contracts, and outsourcing deals. Each contract can create risk if a team misses a duty, accepts weak language, or loses track of a deadline.
Risk teams often face a data problem before they face a legal problem. They may know that a contract exists, but not where it sits or what it requires. A shared folder may hold one version, while email holds another. A business unit may also keep a signed copy outside the legal team’s system.
Contract intelligence helps bring this information together. It converts unstructured files into searchable data. The technology also connects contract terms with people, vendors, systems, and business processes.
For example, a bank may need to locate every vendor contract with:
A right to audit
A notification duty after a security event
A weak service credit
A broad subcontracting right
A renewal date within the next six months
A manual search could take weeks. A structured contract system can narrow the review to a focused group of agreements. Legal and risk teams can then make decisions with better context.
This technology does not replace legal judgment. It helps lawyers and risk professionals spend less time locating information. They can spend more time deciding what the information means and what action should follow.
Related articles: What is Contract Risk & How to manage it?
Why Contracts Matter to the Risk Lifecycle
Contracts shape how a financial institution buys services, serves customers, and manages counterparties. Additionally, beyond those choices, a contract sets out rights, duties, remedies, and limits. It captures the risk decisions that leaders make.
For example, a risk policy may call for specific data protection language. The agreement translates that policy into clear, enforceable duties. Those duties may cover encryption, incident notices, audit rights, staff controls, and data deletion.
A policy, standing alone, may leave a material gap where the contract does not support it. That gap may also emerge if no operational process follows from the contract. Effective oversight therefore depends on pairing the legal term with a process that verifies performance.
The Office of the Comptroller of the Currency provides guidance on managing risks associated with third party relationships for national banks and federal savings associations. That guidance calls on banks to manage these relationships across the relationship lifecycle, from planning through termination. See the OCC guidance on third party risk management.
Contracts support that lifecycle in several ways:
They define risk ownership.
A contract can state which party must protect data, meet service levels, or report an event.
They create evidence.
An agreement can show that a bank reviewed a vendor’s controls and secured specific rights.
They set response options.
Termination rights, audit rights, service credits, and indemnities can guide action after a breach.
They create deadlines.
Renewal dates, notice windows, reporting duties, and testing dates need active tracking.
They support consistent decisions.
Clause standards help teams apply the same risk approach across similar relationships.
Consider a critical cloud provider. The vendor may support payment processing or customer identity checks. A missing clear incident notice period can delay the bank’s awareness of an event. Limited audit access can likewise make it difficult for the bank to confirm what happened.
Contract intelligence can flag both issues during review. It can also find similar gaps across older agreements. That gives the risk team a portfolio view instead of a single contract view.
Related articles: How to Manage Risk Effectively with Contract Management
How Teams Identify Contractual Risk
Risk identification starts before signature. Additionally, it begins as soon as a business team requests a new vendor, product, service, or transaction. The organization should ask what could go wrong and which contract terms can reduce that risk.
A structured intake process helps teams collect the right facts. The request should capture the vendor, service type, data involved, business owner, location, expected value, and criticality. These details can guide review depth and approval routing.
A low risk office supply contract may need a short review. Moreover, a cloud hosting agreement may need input from legal, security, privacy, procurement, and operations. Clear routing rules should determine where each request goes.
Contract intelligence can support early identification by:
Comparing proposed terms with approved language
Flagging missing security or privacy provisions
Finding unusual liability or indemnity wording
Identifying restrictions on audits or inspections
Highlighting auto renewal terms
Detecting limits on data access or recovery
Finding subcontracting rights
Linking a contract to a critical service or vendor
Legacy agreements need the same attention. At many institutions, years of contracts are scattered among scanned files, network folders, and email archives. As a result, locating important rights quickly can be difficult when they are buried in those documents.
Teams can make scanned pages searchable by applying optical character recognition (OCR). AI metadata extraction can identify parties, dates, governing law, payment terms, and obligations from that text. Furthermore, the team should validate important fields before relying on them.
A sound identification process follows a simple path:
Collect agreements from known and unknown locations.
Remove duplicate files and separate drafts from signed versions.
Make scanned documents text-searchable.
Extract key terms and assign contract owners.
Tag contracts by vendor, service, risk level, and business unit.
Also, route high risk agreements for human review.
Record open questions and missing documents.
Also, the National Institute of Standards and Technology offers a useful model for managing cybersecurity risk. Its Cybersecurity Framework 2.0 stresses the need to govern, identify, protect, detect, respond, and recover. Contract data supports each function when it shows who must act and what the parties agreed to do.
Identification should not end after signature. New rules, business changes, vendor events, and market shocks can create new risks. Teams need a repeatable way to rescan contract portfolios when conditions change.
Related articles: How to Simplify Contract Review with AI? Comprehensive Guide
How Teams Assess Risk and Set Priorities
Identification produces a list of possible risks. Additionally, assessment then determines which risks need action first. It also helps leaders decide whether to accept, reduce, transfer, or avoid a risk.
Financial institutions rarely have enough resources to review every contract with equal depth. A practical model assigns priority by combining several factors:
Impact on customers
Effect on critical operations
Access to sensitive data
Financial exposure
Regulatory importance
Vendor dependency
Contract length
Ease of replacement
Strength of available remedies
A risk score can help with triage, but the score should not make the decision alone. A contract may receive a moderate score because each issue looks small. Several moderate issues together may still create a serious problem.
For example, a vendor contract may contain a narrow audit right, a long incident notice period, and a low service credit. Each gap may appear manageable. Together, they could leave the bank without timely information or useful remedies during a major outage.
Contract intelligence can compare terms against a legal playbook. A playbook defines preferred language, fallback positions, approval triggers, and escalation rules. It gives reviewers a consistent starting point.
The system may flag a clause because it:
Deviates from approved language
Creates an unlimited financial obligation
Lacks a required insurance level
Uses a governing law that needs approval
Omits data return or deletion duties
Gives a vendor broad access to subcontractors
Limits a regulator’s access to records
The reviewer still needs context. A vendor may reject the preferred clause but offer a strong alternative. The business may also accept a different position because the service has unique value. The system should capture that decision, its owner, and its reason.
The Basel Committee on Banking Supervision has published principles addressing operational resilience. Its guidance on operational resilience calls on banks to identify important business services and manage risks that could disrupt them. Contract review should connect with that work.
A useful assessment process includes:
Define the risk category and affected service.
Confirm that the contract language matches the source document.
Next, test those provisions against the relevant policy and playbook rules.
Consider the resulting financial, operational, customer, and regulatory consequences.
Give an owner responsibility and set a due date.
Select a response that is consistent with the institution’s risk appetite.
Document the decision, retaining the evidence needed to support it.
Taken together, these steps make contract review a documented risk decision. It also gives audit teams a traceable record of how each issue reached its outcome.
Related reading: How IT and Professional Services Cut Operational Risks
How Teams Mitigate Contract Risk
Mitigation reduces the chance or impact of a harmful event. Additionally, the appropriate response depends on the risk, the relationship, and the organization’s risk appetite.
Legal teams may negotiate stronger terms before signature. They may also amend existing agreements after a new rule, control gap, or vendor event. Business teams may change a process, add a control, or move work to another provider.
Common contract based mitigation actions include:
Add a required security provision
Shorten an incident reporting period
Raise insurance limits
Add audit or inspection rights
Limit subcontractor use
Require business continuity testing
Clarify recovery time targets
Add data deletion duties
Set stronger service credits
Create termination rights for serious failures
A contract system can help teams manage these actions at scale. Suppose a new internal policy requires a specific privacy clause. The legal team can search for agreements that lack the clause. It can then group those contracts by vendor, service, renewal date, and business owner.
The team may choose different responses. It could amend a critical vendor contract at once. Moreover, for a lower-risk agreement, the team might wait until renewal. It could accept the gap for a short period with approval and a documented compensating control.
This approach avoids two common errors. The first error treats every issue as urgent, which overwhelms the team. The second error leaves risk untouched because no one can see the full population.
Mitigation also needs careful negotiation. AI can identify comparable past positions and suggest fallback language that has already been approved. Before any recommendation goes to a counterparty, a lawyer should review it. It must not generate unsupported promises or propose terms beyond the organization’s authority.
The Financial Stability Board's work in financial services addresses operational resilience, including dependencies on third parties. In its third party risk guidance, the Board emphasizes that firms need to understand their dependencies and manage the risks those relationships create. By mapping the contracts, teams can see where those dependencies lie and which protections govern them.
Effective mitigation involves four steps:
Describe the problem in plain language.
Choose a response proportionate to the risk at issue.
Give a clearly identified individual responsibility for completing the action.
Establish a deadline and retain evidence that the action was completed.
Completing a task does not necessarily resolve the underlying risk. Teams should subsequently verify that the new term works as intended in practice. They should also verify that the change has reached the relevant systems and personnel.
Further reading: How Tech Firms Can Use Contracts to Cut Risk in 2026
How Teams Monitor Controls and Obligations
Risk management continues after execution. Additionally, teams must also track what each party promised and confirm that performance matches the agreement.
Contracts can create hundreds of recurring duties. A vendor’s obligations may include delivering reports, completing tests, maintaining insurance, meeting uptime targets, or notifying the bank about an event. A financial institution is responsible for paying fees, providing data, or sending renewal notices.
Missed duties can create direct costs. These failures can also weaken oversight and damage trust with regulators. A reminder in one person’s calendar cannot provide enough control for a large contract portfolio.
Obligation management helps assign each duty to an owner. It records the due date, source clause, evidence needed, and escalation path. Moreover, automated alerts can notify owners before a deadline. Escalations can reach managers when an item remains open.
Useful monitoring data includes:
Service level results
Missed deliverables
Incident notices
Audit reports
Insurance certificates
Business continuity tests
Compliance attestations
Payment and fee changes
Renewal and termination dates
Open remediation tasks
Dashboards can show risk by vendor, service, region, or business unit. They can likewise show overdue tasks and agreements nearing renewal. Leaders can then focus on the areas that need action.
The Securities and Exchange Commission requires certain public companies to disclose material cybersecurity incidents and related risk management information. Its cybersecurity disclosure rules show why contract data and incident processes need close alignment. A vendor event may affect reporting duties, customer communications, and internal escalation.
Monitoring also needs evidence quality. Furthermore, a vendor email may not prove that a required control worked. The owner should know what evidence the contract requires and where to store it. A secure record can link evidence to the obligation and review date.
Also, teams should review monitoring rules when contracts change. An amendment may alter a service level, notice period, or owner. If the system does not update the obligation record, the institution may monitor the wrong requirement.
Good monitoring asks three simple questions:
What did the contract require?
Did performance, in practice, stay aligned with the agreement?
When it did not, what response is warranted?
Together, they tie monitoring to business outcomes. They also help teams move from passive record keeping to active risk control.
Related articles: Why Telecom’s Contract Management Maturity Sets It Apart
How Teams Report Risk to Leaders and Regulators
Reporting turns contract information into a decision tool. Additionally, legal and risk teams, meanwhile, need reports that explain exposure rather than merely display data without meaning.
Senior leaders may want to know which critical vendors lack strong recovery duties. For the board, trends in material contract exceptions may matter most. An auditor may instead seek evidence that review, approval, and remediation occurred.
A useful report should make the following points clear:
Which risk is present?
Which service or customer could be affected?
Who is accountable for the relevant team or relationship?
Which contractual provision creates the risk?
Which remediation items are still open?
What is the expected completion date?
What evidence substantiates the reported status?
The appropriate level of detail depends on the audience. For the board, reporting may emphasize trends and the most significant exposures. Legal teams typically need clause deviations and negotiation status. Operations teams, in contrast, usually focus on overdue obligations and actual service results.
A common contract intelligence data set can underpin each of these views. Using one data set reduces manual spreadsheet work and limits inconsistencies in reported figures. It also gives teams a way to trace each summary back to the original contract and supporting evidence.
Reports should use clear categories. For example, an institution might group issues as data security, service continuity, financial exposure, regulatory access, privacy, and termination rights. Consistent categories allow leaders to compare trends over time.
Teams should also report uncertainty. A missing contract, unknown owner, or unverified obligation creates its own risk. Leaders need to see data quality gaps because those gaps can hide larger exposure.
The report process should include review controls:
Confirm the reporting period.
Check records for duplicate entries and stale data.
Subject matter experts should validate high-impact findings.
Note any changes from the prior report.
Capture the identity of the person who approved the final view.
Retain source evidence for later review.
The Federal Reserve, FDIC, and OCC have issued guidance on third-party relationships. This interagency guidance sets expectations for planning, due diligence, contracting, monitoring, and termination. Contract intelligence can support these activities, but governance and accountability remain essential.
Strong reporting creates a feedback loop. Leaders see recurring gaps, then update policies, templates, playbooks, and training. The next contract review can reflect those lessons.
Related articles: How Contract Intelligence Transforms Healthcare Operations
How to Choose Contract Intelligence Software
Generic contract management software can centralize agreements, automate approvals, track obligations, and provide audit trails. Additionally, it can also reduce manual work during drafting, review, signing, and renewal. These functions create the foundation for better risk management.
Look for features that fit financial services work. AI review should flag missing provisions, unusual terms, and policy deviations. AI summaries should show key risks, dates, liabilities, governing law, and duties in plain language.
Use bulk import and OCR to bring older agreements into a single repository. Metadata extraction identifies parties, dates, jurisdictions, payment terms, and obligations. For records with significant impact, keep a human in the validation loop.
The platform supports AI drafting, contract review, clause recommendations, summaries, metadata extraction, playbooks, approval workflows, obligation tracking, alerts, search, role based access, and audit trails. These features help legal, risk, procurement, and operations teams work from one controlled contract record.
Ready to make contract management more efficient? For more details, visit Volody's.
FAQ
How does a bank use contract intelligence?
Additionally, contract intelligence helps a bank find and understand information in agreements. It can identify risk terms, obligations, deadlines, owners, and policy gaps across a contract portfolio.
How does third party risk management benefit from contract intelligence?
It ties vendor contracts to the services they support, as well as the responsible owners, controls, and duties. This gives teams a basis for assessing risk before signature and monitoring performance after execution.
Does using contract intelligence eliminate the need for a lawyer?
No. It can reduce search, sorting, and first review work. Lawyers still need to interpret complex terms, make judgment calls, approve exceptions, and guide negotiations.
Moreover, how can AI identify risks in contracts?
AI can compare contract language with approved clauses and review rules. It may flag missing terms, unusual wording, weak remedies, or provisions that need human review.
What contract data should financial institutions track?
Teams should track parties, services, owners, dates, fees, obligations, service levels, audit rights, security duties, renewal terms, liability limits, and governing law.
How can teams manage old paper and scanned contracts?
They can use bulk import and OCR to convert files into searchable records. Teams should then validate key fields and assign owners before using the data for formal decisions.
Furthermore, which controls belong in a contract intelligence platform?
Important controls include role based access, encryption, audit trails, version history, approval records, backup processes, and secure integrations. Access should match each person’s role and business need.
What role can contract intelligence play in an audit?
It brings contract terms together with approvals, review notes, obligations, evidence, and remediation tasks. From the source agreement, auditors can follow a decision through to its current status.
How should a financial institution begin a project using contract intelligence?
Start with a focused contract group, such as critical technology vendors. Define risk rules, clean the data, assign owners, test extraction accuracy, and expand after the process proves reliable. Engage stakeholders now to establish a controlled, scalable contract intelligence program.
About the Company
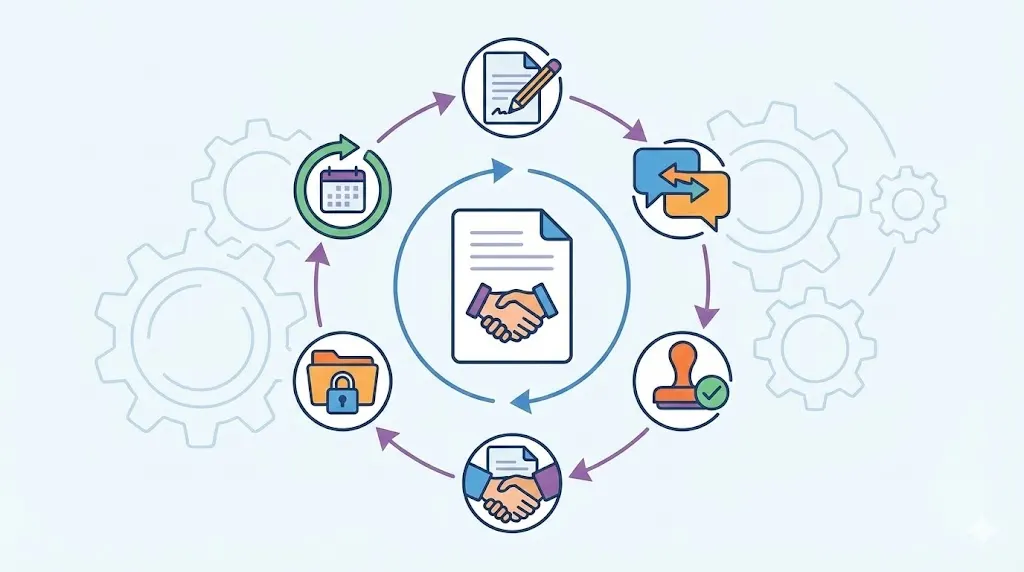
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.


" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)