
Samya Namdeo

A well-structured NDA establishes enforceable controls for sensitive information exchanged in business relationships. It defines permitted use, access, disclosure, retention, and remedies while aligning legal protections with operational realities. This guide provides a practical framework for drafting, reviewing, enforcing, and managing NDAs throughout their lifecycle.
TL;DR
An NDA defines protected information and limits its use, access, and disclosure.
Choose a unilateral NDA when one party shares information, or a mutual NDA when both parties share.
Clear definitions, exclusions, time limits, and remedies support stronger NDA enforceability.
Common challenges include vague terms, excessive limits, lawful disclosures, and weak breach evidence.
A careful NDA review process checks authority, purpose, access, duration, remedies, and exit steps.
Contract management software helps teams store, approve, monitor, and renew NDAs with less manual work.
What an NDA Protects and How It Works
An NDA confidentiality agreement creates duties around private information. The term NDA means “non-disclosure agreement.” It may also appear as a confidentiality agreement.
The agreement names the parties, explains the information, and limits its use. It can support NDA trade secret protection, but it does not create ownership by itself.
Confidential information and trade secrets
Confidential information includes knowledge that a business does not share publicly. An NDA should describe this information in clear, useful categories.
Examples include business plans, customer lists, pricing, passwords, and financial data. They may also include inventions, source code, algorithms, product designs, and test results.
A trade secret is valuable information kept secret through reasonable care. It might include a process, formula, method, or software design. The NDA should support secrecy, but daily security controls matter too.
An NDA can also protect patent rights during early discussions. Public disclosure may affect patent rights in some places. Confidential discussions can reduce that risk before legal patent advice is complete.
The parties and their obligations
The disclosing party shares the protected information. The receiving party obtains it for a stated business purpose. A mutual NDA agreement gives both parties these roles.
The receiving party usually must keep information private. It may use the information only for the agreed purpose. It should limit access to staff, advisers, or contractors with a real need.
Those people should face similar confidentiality duties. The receiving party may also need reasonable security controls. These controls can include access limits, secure storage, and careful file sharing.
Many NDAs require the receiving party to return or destroy information. This duty may apply when talks end or the disclosing party asks. Some records may remain because law or company policy requires retention.
When confidentiality becomes a legal duty
A signed NDA creates contractual duties between the parties. Those duties begin according to the agreement’s terms. Some agreements protect information shared before signing, while others do not.
A breach occurs when someone uses or shares protected information without permission. The disclosing party may seek an injunction. An injunction is a court order that can stop conduct or require action.
Damages may also be available under applicable law. They can cover losses caused by misuse or unauthorized disclosure. The NDA may state that some harm would be difficult to measure.
The agreement does not guarantee success in court. Courts examine the wording, facts, and local law. Clear duties make the parties’ positions easier to understand.
Information covered by a practical NDA
A practical NDA checklist starts with the protected information. It then states the permitted use, access rules, confidentiality duty, and possible remedies.
The checklist should cover business records, software, plans, customer data, and technical material. It should also address oral disclosures, copies, notes, and related work products. The permitted use should match the real business discussion.
The agreement should explain lawful exceptions and required disclosures. It should state how long duties continue. It should also describe return, destruction, court relief, and damages.
Related Article: NDAs (Non-Disclosure Agreements): A guide to secrecy
When Businesses Use an NDA
Businesses use NDAs before sharing information with people outside normal access. The agreement creates a clear boundary before talks begin. It can also support trust during a sensitive project.
An NDA does not replace a service contract, employment agreement, or data agreement. Each document serves a different purpose. The NDA focuses on confidentiality and permitted use.
Early discussions and potential transactions
Companies often use NDAs before discussing a partnership or investment. They may share financial results, customer data, product plans, or growth plans. This information can shape another party’s business decisions.
An NDA may support acquisition talks, licensing discussions, and vendor reviews. It can also cover a possible joint venture or commercial deal. The parties can share information without granting broad business rights.
A buyer may review records during due diligence. Due diligence means checking a business before completing a deal. The NDA should limit that information to the review purpose.
Investors may receive plans, forecasts, and invention details. Vendors may see processes, prices, or technical needs. Each setting requires a clear purpose and suitable access rules.
Employment and contractor relationships
Employers use NDAs to protect internal information during work. Employees may access customer records, product plans, systems, and business methods. Contractors may see similar information while serving several clients.
The NDA should match the person’s real access. A developer may need code and product plans. A sales contractor may need pricing, customer data, and market plans.
An employment NDA should not block lawful work after employment ends. It should not act as a hidden non-compete. A non-compete limits future work, while an NDA limits disclosure or use.
Employers should pair the NDA with access controls. They should remove access when work ends. They should also explain how staff must handle files, passwords, and copies.
Research, development, and technology sharing
Research teams may sign NDAs before sharing invention details. They may discuss prototypes, test results, methods, or unpublished data. An NDA can help keep these discussions private.
Software teams may share source code, technical specifications, and development processes. A SaaS NDA may also cover security details, roadmaps, pricing, and customer information. SaaS means software delivered through an online service.
Licensing talks often involve technical and commercial information. The agreement should separate evaluation from later use. A recipient may review a technology without receiving a right to build or sell it.
Research partners should address publication plans. Academic or public research may require later disclosure. The NDA should allow agreed publications while protecting genuinely private material.
How NDA needs differ across business relationships
An employee may receive broad access for daily work. That NDA needs strong use limits and clear exit duties. It should also fit employment and privacy rules.
A contractor may receive narrower access for one project. The NDA should name that project and restrict copying. It should also cover subcontractors and shared workspaces.
A potential partner may exchange information both ways. That relationship often needs a mutual NDA agreement. The agreement should cover each party’s separate business information.
An investor may review plans without operating the business. That NDA may focus on financial records, forecasts, and inventions. The parties should set careful rules for advisers and portfolio discussions.
Related Article: Understanding Non-Disclosure Agreements: Key Insights
Choosing Between Mutual and One-Way NDAs
The right NDA agreement type depends on expected information flow. It also depends on the relationship, purpose, and risk. A short discussion may need less detail than a long project.
One-way confidentiality agreements
A unilateral NDA agreement protects information from one main disclosing party. The other party receives information and accepts confidentiality duties. This structure suits many employer, vendor, and investor discussions.
For example, a company may share product plans with a contractor. The contractor may not share comparable confidential information. A one-way agreement keeps duties focused on that real exchange.
The agreement should still address advisers and subcontractors. It should explain access, permitted use, and return duties. It should also cover information copied or created during the review.
A one-way form may be easier to review and approve. It avoids placing duties on a party that shares nothing. However, the form should change if information flows later change.
Mutual confidentiality agreements
A mutual NDA protects information shared by both parties. Each party becomes a discloser and a recipient. This structure fits partnerships, SaaS relationships, and research projects.
A SaaS provider may share product details and security information. The customer may share business data, user needs, or planned integrations. Both sides need protection during those discussions.
Mutual terms should apply evenly unless a real reason supports different rules. The agreement should define each party’s permitted purpose. It should also cover advisers, service providers, and related companies.
A mutual NDA does not mean both sides share equal amounts. It means both sides receive protection when they disclose information. The duties can remain reciprocal even when risk differs.
Matching the agreement to the relationship
Start by asking who will share information. Then ask how sensitive the information is. Next, set the needed protection period and confirm whether both parties will disclose.
For one disclosing company and one receiving contractor, use a unilateral form. For two companies sharing code and plans, use a mutual form. For an existing deal, place the NDA beside the main contract when duties connect.
Consider negotiation leverage and risk allocation. A powerful party may suggest broad terms for convenience. The other party should test whether those terms fit the real exchange.
Some NDAs stand alone before a transaction. Others form part of a services, license, or supply contract. Related contracts should use consistent terms and avoid conflicting duties.
Avoiding unnecessary restrictions
An NDA should protect legitimate confidential information. It should not restrict lawful speech, ordinary skill, or independent work. Broad language can create disputes without improving real protection.
The agreement should limit use for a defined purpose. It should not ban every use of general knowledge. It should also avoid restrictions that function like an unspoken non-compete.
A useful decision matrix can guide the choice. One party sharing sensitive information usually points toward a unilateral form. Both parties sharing sensitive information points toward a mutual form.
Short protection needs suit a limited review. Long protection needs suit trade secrets and continuing secrecy. High sensitivity calls for tighter access, stronger security, and clearer remedies.
Related Article: Types of NDA Explained: Choose the Right One for You
5 Key Challenges in NDA Drafting and Enforcement
NDA drafting often fails through small wording gaps. Those gaps can weaken trust and raise enforcement costs. Good terms connect each risk with a workable rule.
1. Defining confidential information precisely
A broad definition can capture useful information, but vague wording creates doubt. A narrow definition may leave important material outside protection. The agreement should use clear categories and examples.
Marking rules can help, but they should not create unfair traps. Oral disclosures need a clear confirmation process. Notes, copies, and summaries should receive matching treatment.
The drafting consequence is simple. Unclear definitions make breach claims harder to prove. Clear categories make review, training, and enforcement easier.
2. Setting practical duration and scope
The NDA should separate the agreement term from confidentiality duration. The business relationship may end before secrecy duties end. Trade secrets may need protection while they remain secret.
The agreement should address geography where relevant. It should also limit recipients, copying, and reverse engineering. These rules should match the information and the work.
Overlong limits may draw negotiation objections. Very short limits may expose valuable information too soon. The drafting consequence is a poor balance between protection and reasonableness.
3. Handling exclusions and lawful disclosures
Common exclusions cover public information and prior knowledge. They may also cover independent development and lawful receipt from another source. These exclusions prevent the NDA from claiming too much.
A recipient may face a court order or legal demand. The NDA should permit that disclosure when law requires it. It may require notice, unless notice is legally barred.
The enforcement consequence is clearer evidence. Each party can test whether an exclusion applies. Without these rules, ordinary facts may trigger unnecessary disputes.
4. Protecting whistleblowing and regulatory rights
An NDA should not block reports protected by law. Those reports may involve regulators, law enforcement, courts, or safety concerns. Local rules may also protect certain workplace disclosures.
The agreement should allow legally protected communication. It should avoid threatening penalties for lawful reporting. Legal counsel can help address special rules in each location.
The drafting consequence is lower risk of an unlawful restriction. It also protects the agreement from an overly broad reading. A lawful NDA supports secrecy without silencing protected conduct.
5. Proving misuse after a breach
A breach claim needs evidence of access, use, or disclosure. Useful evidence may include access logs, copied files, emails, and witness accounts. The evidence should connect the conduct to protected information.
The disclosing party must often show loss or likely harm. That may involve lost sales, damaged negotiations, or unfair competition. The facts can become harder to prove months after the event.
The enforcement consequence is clear. Weak records can undermine a strong written NDA. Access logs, disclosure records, and prompt notices improve the response.
Related Article: Drafting Effective NDAs for 2026: A Strategic Guide
Building Clear and Balanced NDA Terms
Strong NDA terms reflect the actual information exchange. They do not rely on a copied NDA template alone. A template should provide structure, not replace careful review.
A precise definition of protected information
Use clear categories that fit the business. These may include code, plans, customer data, pricing, research, and technical designs. Add examples when they help readers identify protected material.
Marking requirements can support better handling. The NDA should explain whether marked files receive automatic protection. It should also explain how parties identify oral or visual disclosures.
Some information may remain protected without a label. This can matter during meetings, demonstrations, or live system reviews. The agreement should avoid losing protection because someone missed a stamp.
The definition should cover copies, notes, analyses, and extracts. It should also address information created from protected material. These details close common gaps during review and use.
Permitted use and access controls
State the exact purpose for receiving the information. A party reviewing a product should not gain permission to sell or copy it. Purpose limits make misuse easier to identify.
Use a need-to-know access rule. This means only people who need the information may receive it. Employees, advisers, and contractors should face matching confidentiality duties.
Set reasonable security expectations. These may include password controls, limited downloads, and secure transfer. Reverse engineering and unapproved copying may need express limits.
Access rules should match the information’s sensitivity. Customer data may need stronger controls than a general product brochure. Practical rules work better than demands a team cannot follow.
Exclusions, disclosures, and required cooperation
List standard exclusions in plain language. Public information, prior knowledge, independent development, and lawful third-party receipt commonly appear. The receiving party may need records supporting an exclusion.
Required disclosure terms should address legal demands. They may require prompt notice and reasonable cooperation. Notice must not be required when law forbids it.
Professional advisers may need access during a transaction. The NDA should permit that access under matching duties. The receiving party should remain responsible for its chosen representatives.
Cooperation may include helping protect an invention or responding to an inquiry. The agreement should define reasonable steps. It should not demand unlimited cost or effort.
Remedies, ownership, and relationship boundaries
The disclosing party keeps ownership of its confidential information. Sharing information does not grant a license or transfer intellectual property. The NDA should state this directly.
Remedies may include an injunction and damages. The agreement may also allow other legal remedies. Local law decides whether courts grant a requested remedy.
The NDA should not promise that a transaction will happen. It should also state whether either party may stop discussions. Confidentiality can continue after talks end.
A clause planning sequence keeps drafting focused. Define information first, then set use, access, exclusions, duration, remedies, and governing law. Governing law names which legal system guides the agreement.
Related Article: Essential Elements of a Confidentiality Agreement Explained
NDA Review and Implementation Best Practices
A good NDA review process checks business facts and legal terms together. Reviewers should ask what information will move, who will see it, and why. They should also confirm how teams will follow the agreement.
Before signing
Confirm that each signer has authority to bind the party. Check the company name, address, and related agreements. Correct identity errors before signature.
Review the defined information against the planned exchange. Test whether staff can meet the access and security duties. Remove obligations that the business cannot track or perform.
Check governing law and the selected court location. “Jurisdiction” means the place where a dispute may be heard. Cross-border deals may need extra legal review.
Consider qualified legal counsel for higher-risk matters. This includes trade secrets, regulated data, inventions, employees, and international parties. Legal review helps identify local rules and hidden conflicts.
During information sharing
Use secure transfer methods for sensitive files. Apply access permissions before sending materials. Keep a record of who received each important disclosure.
Label documents when the NDA requires labels. Explain how staff should handle oral, visual, or unmarked information. A short team briefing can prevent avoidable mistakes.
Keep copies in approved systems. Avoid personal email, open links, and unmanaged devices. Review access when project roles change.
The disclosing party should track what it shares. The receiving party should track where information goes. These records support later questions and any breach response.
When the relationship changes or ends
The disclosing party may request return or destruction. The receiving party should follow the stated process and confirm completion. Legal retention needs may require limited copies.
Revoke access during offboarding. Remove shared links, system rights, and local copies where possible. Remind departing staff about continuing duties.
Review renewal dates and survival periods. Some NDAs expire while confidentiality duties continue. The record should show both dates clearly.
Preserve evidence when a dispute may arise. Do not delete relevant emails, logs, or files. A careful exit process protects both parties.
A practical review checklist
A useful checklist begins with signer authority and accurate party names. It then checks defined information, permitted use, access, and exclusions. Reviewers should confirm duration, remedies, and governing law.
The checklist should ask whether oral disclosures receive protection. It should test return, destruction, retention, and access removal. It should also identify related employment, service, data, or license contracts.
The final check covers daily ownership. Someone should know who sends notices and tracks duties. Without an owner, even clear NDA terms can fail.
Related Article: How to Protect Sensitive Contracts: Best Practices
Managing NDA Workflows at Scale
Large teams may handle many NDAs each month. Email alone makes status, access, and renewal details hard to find. A repeatable workflow creates one reliable record.
Implementing a repeatable NDA workflow
Start with intake, then select an approved NDA template. Route the draft for business and legal approval. Send the final version for signature.
After signing, store the agreement with its key details. Record parties, purpose, dates, information type, and owners. Link related projects or contracts when needed.
Next, track renewal dates and confidentiality periods. Review access during the project and after role changes. At the end, manage retention, destruction, or approved record storage.
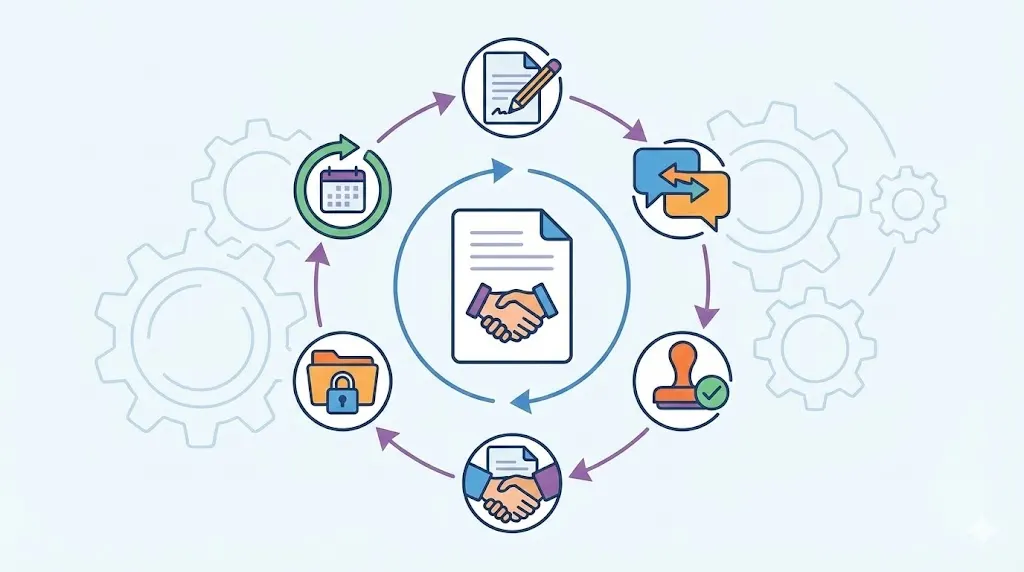
The full process sequence is intake, drafting, approval, signature, storage, renewal tracking, access review, and retention or destruction. Each step should have an owner. Automated reminders can reduce missed actions.
Tracking obligations throughout the agreement lifecycle
Teams should monitor expiration status and continuing duties. They should also track access permissions, required notices, and return requests. A central record makes these details easier to review.
Audit trails show who changed, approved, or accessed the agreement. Related records can show shared files, projects, and disclosure history. These records support evidence of compliance.
Retention rules should fit legal and business needs. Not every NDA needs the same storage period. A clear policy helps teams avoid both early deletion and needless storage.
Related Article: Contract Permissions: Managing Access with Precision
Why Contract Management Software Matters
Contract management software gives teams one place for NDA records. It can connect templates, signed agreements, dates, obligations, and related files. Search tools help users find the right record quickly.
It can also standardize approval and signature steps. Reminders can flag renewals, return duties, and continuing confidentiality periods. Audit trails show key actions across the NDA review process.
Central storage: Keep NDA templates, signed files, dates, and related records together. Searchable records reduce time spent checking scattered emails and folders.
Workflow control: Route NDAs to the right reviewers before signature. Automated reminders help teams follow approvals, signatures, and renewal tasks.
Obligation tracking: Record confidentiality periods, access duties, return requests, and destruction steps. Teams can see open actions before they become missed commitments.
Better oversight: Review NDA status across teams, projects, and business units. Reports can show pending approvals, expired agreements, and upcoming actions.
Lower manual work: Connect NDA data with access reviews, audit trails, and other contract records. This helps legal and business teams manage work consistently.
Contract management software does not replace sound NDA drafting. It helps teams apply those terms after signing. The result is better visibility across the full agreement lifecycle.
Volody’s CLM Software supports NDA work with a central contract repository, AI Contract Summaries, and Approval Workflow Automation. The repository stores signed NDAs with search access. AI summaries highlight obligations, renewal dates, and key risks. Automated routing sends each NDA to the right reviewers.
For example, a SaaS company can store a mutual NDA centrally. The team can route it for approval, then track its confidentiality period and access review.
Want to see how contract management software can simplify your legal workflows? Check out Volody's CLM Software.
FAQ
What is a SaaS NDA?
A SaaS NDA is a non-disclosure agreement for software or cloud service discussions. It may protect source code, algorithms, security details, roadmaps, pricing, and customer data. SaaS NDAs are often mutual because both companies may share sensitive information. The agreement should match the service, data, users, and planned access.
Is an NDA for software development required?
An NDA for software development is not always legally required. It can reduce the risk of unauthorized disclosure or use. It helps when developers receive unpublished code, product plans, or technical details. The NDA should work with intellectual property assignment, security, and data protection terms.
How do you create a SaaS NDA?
Start by naming the parties and describing the planned information exchange. Define confidential information, permitted use, access, exclusions, duration, and remedies. Add rules for required disclosures, security, return, and destruction. Legal review can help match the NDA with each location and business relationship.
Can you write your own NDA?
You can write your own NDA for a simple, limited information exchange. A carefully adapted NDA template can provide a useful starting point. Generic language may omit exclusions, oral disclosure rules, or local requirements. Seek legal review for trade secrets, inventions, regulated data, employees, or international parties.
Can an NDA protect an invention before a patent application?
An NDA can limit premature public disclosure of an invention. This may help preserve patent rights in some jurisdictions. It does not replace patent advice or a filing plan. The NDA should identify invention details and restrict unauthorized use, copying, and sharing.
Can an NDA cover information shared verbally?
An NDA can cover verbal information when its definition includes oral disclosures. It should explain how speakers identify or confirm protected content. Some agreements require written confirmation after a meeting. Clear procedures reduce disputes about conversations, demonstrations, and presentations.
What are common NDA breach consequences?
NDA breach consequences may include a demand to stop disclosure or return information. The disclosing party may seek an injunction, damages, or other legal remedies. Contract terms and local law control the available options. Prompt records and notice can support a stronger response.
How long should an NDA last?
Build an NDA program with terms, workflows, and contract management controls that protect sensitive information, strengthen oversight, and reduce manual work across its lifecycle.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.


" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)