
A precisely tailored NDA is essential to protecting sensitive information while establishing clear, enforceable obligations. Effective agreements reflect the project, relationship, industry, and level of risk involved. They define what must remain confidential, how recipients may use it, and what happens if obligations are breached. This guide provides a practical framework for drafting, executing, and managing an NDA.
Related Article: Non-Disclosure Agreements: A Practical Guide
TL;DR
Define trade secrets, customer lists, financial data, technical information, and business plans with clear, useful categories.
Match the NDA structure to each relationship, whether disclosure flows one way, both ways, or among several parties.
Customize access rules, security duties, exclusions, disclosure steps, confidentiality periods, and long-term obligations.
Protect trade secrets through access controls, employee training, secure systems, vendor rules, monitoring, and careful information labeling.
Cover return duties, breach consequences, remedies, governing law, jurisdiction, dispute steps, signatures, and final document delivery.
Use NDA management software to track approvals, signed copies, disclosures, renewals, access reviews, and closure tasks.
Define the Information and Purpose Precisely
A broad NDA does not always provide strong protection. Vague words can make enforcement harder. The recipient may claim uncertainty about what the agreement covers.
Name the information that matters most. Consider business plans, customer lists, pricing, financial data, product roadmaps, source code, and technical information. Include trade secrets when the information gains value from staying unknown.
The NDA should also explain why the parties share information. A clear purpose limits use and guides later disputes. It also helps teams decide which custom NDA clauses fit the deal.
Identify Protected Information by Category
Group protected information into practical categories. Business information may include plans, forecasts, pricing, and customer records. Technical information may include designs, source code, formulas, test results, and product plans.
Operational information can cover processes, supplier terms, and service methods. Financial information may include budgets, margins, and funding details. Personal information may include employee or customer records.
Do not copy the best NDA templates for businesses without review. A template can miss risks in your field. Industry-specific NDA examples can reveal useful categories, but counsel should adapt them.
Link Disclosure to a Permitted Purpose
State the exact reason for disclosure. The purpose may involve a product review, hiring process, sale discussion, or joint project. It may also cover employment, consulting, investment, or supplier work.
The recipient should use information only for that purpose. Ban unrelated commercial, competitive, or personal use. Add limits on copying, testing, reverse engineering, or product development when needed.
A clear purpose also supports employee confidentiality agreements customization. Employees may need broad work-related access. Contractors may need access only to a defined task.
Document and Label Disclosures
Cover every disclosure format. Confidential information may appear in writing, speech, images, systems, devices, or physical samples. Oral disclosures need a clear follow-up process.
Use confidential markings when practical. Record important disclosures in a log or data room. Confirm sensitive oral disclosures in writing within an agreed period.
Access records can show who viewed information. They can also show when the recipient received it. These records support enforceable confidentiality agreements during a dispute.
Protected categories: Name business, technical, financial, personal, and trade secret information.
Disclosure formats: Cover written, oral, visual, electronic, and physical disclosures.
Permitted purpose: State the project, review, role, deal, or service that allows use.
Labeling process: Set rules for markings, follow-up notices, logs, and access records.
Related Article: Drafting Effective NDAs for 2026: A Strategic Guide
Select the Right NDA Structure for the Relationship
The right NDA structure follows the flow of information. A one-way deal may need a unilateral NDA. A shared project may need a mutual NDA. Several parties may need multilateral terms.
Do not choose a form based only on convenience. Review who discloses information and who receives it. Also compare the value and sensitivity of each party’s information.
Employee confidentiality agreements customization often needs special care. Employees may access many systems during their work. Vendors and investors usually need narrower access.
Choose Unilateral, Mutual, or Multilateral Terms
A unilateral NDA protects information moving from one party to another. It often suits a company and contractor, vendor, investor, or job candidate. The receiving party carries most confidentiality duties.
A mutual NDA protects information shared by both sides. It suits partnerships, joint development, and early deal talks. Each party must protect the other party’s information.
A multilateral NDA covers three or more parties. It should identify each disclosing and receiving party. It should also explain whether all parties share equal duties.
Tailor Duties to Each Relationship
Employees may need access across several business areas. Their agreement should address work product, systems, devices, and departure procedures. Contractors may need stricter limits on copying and subcontractor access.
Suppliers may receive designs, forecasts, or customer details. Investors may review financial and growth information. Strategic partners may receive technical plans and market data.
Include representatives when they may access protected information. Representatives may include affiliates, advisers, consultants, and subcontractors. The main recipient should remain responsible for their conduct.
NDA structure | Common use case | Main parties | Drafting focus |
|---|---|---|---|
Unilateral | Hiring, investment review, vendor work | One discloser and one recipient | Define recipient duties and approved use |
Mutual | Partnerships, joint projects, deal talks | Two disclosing and receiving parties | Balance duties without ignoring different risks |
Multilateral | Consortiums, shared research, complex transactions | Three or more parties | Identify each party’s role and responsibility |
Related Article: Types of NDA Explained: Choose the Right One for You
Customize Core Confidentiality Obligations
An NDA should describe what the receiving party must do. The duties should cover protection, access, use, copying, and disclosure. They should also fit the information’s sensitivity.
Contract terms do not replace technical security. A promise to protect data cannot secure a weak system. Pair legal duties with access controls, safe storage, and staff training.
Set Access and Use Restrictions
Use need-to-know access rules. Only people supporting the permitted purpose should view the information. Limit access when a team member’s role changes.
Control copying, downloads, printing, and transfers. Ban reverse engineering when the disclosure involves software, products, or samples. Also address competitive use when market harm remains possible.
Set clear rules for representatives. Require approval before sharing information with them. Make the recipient responsible for their confidentiality duties.
Add Security and Incident Duties
Describe administrative, physical, and technical safeguards. These may include staff training, secure storage, strong access controls, and device protections. Match the safeguards to the information and business risk.
Require prompt notice of suspected incidents. The notice should identify known facts and support quick investigation. It should also explain cooperation duties during response efforts.
Avoid relying only on “reasonable care.” That phrase may lack useful detail. Add practical duties for access, storage, transfer, copying, and incident reporting.
Access: Limit viewing to approved people with a genuine business need.
Permitted use: Restrict use to the stated project, review, role, or transaction.
Representatives: Require recipient responsibility for advisers, affiliates, and subcontractors.
Security: Set suitable administrative, physical, and technical safeguards.
Incidents: Require prompt notice, cooperation, investigation, and corrective action.
Related Article: Essential Guide to the Confidentiality Clause in Contracts
Address Exclusions, Disclosures, and Evidence
Every NDA needs sensible exclusions. Without them, the agreement may cover information that already belongs outside the deal. Overly broad terms can also create legal and business problems.
Common exclusions cover public information, prior knowledge, independent development, and lawful third-party receipt. The agreement may also exclude information approved for release.
The receiving party should prove an exclusion applies. This prevents vague claims from becoming loopholes. Dated files, project notes, and earlier records can support that proof.
Define the Standard Exclusions
Public information may fall outside the NDA after lawful publication. Information already known before disclosure may also qualify. The recipient should show that prior knowledge existed before receiving it.
Independent development requires clear records. Product notes, source files, and dated research may help. Lawful receipt from another source also needs supporting evidence.
An authorized release should come from the disclosing party. The release should identify what information may be shared. It should not create a wider release by accident.
Handle Legally Required Disclosures
An NDA should address subpoenas, court orders, and regulator requests. It should also respect protected whistleblowing and lawful regulatory cooperation. The contract should not block rights that the law protects.
Require notice when the law allows notice. Give the disclosing party time to seek a protective order. The recipient should disclose only the legally required portion.
The recipient should cooperate with reasonable protection efforts. It should also keep the disclosed information private where possible. These steps reduce unnecessary exposure.
Preserve a Clear Disclosure Record
Use written confirmations for important disclosures. Data rooms can record access, downloads, and approved users. Disclosure schedules can list files, samples, and other materials.
Keep records of approved recipients. Save copies of notices and release decisions. These records can support the agreement if the parties later disagree.
Good records also improve daily control. Legal teams can find what was shared. Business teams can confirm who may access it.
Check the claim: Ask whether the information was public, known, developed, received, or released lawfully.
Request proof: Require dated records that support prior knowledge or independent development.
Give notice: Notify the disclosing party when law permits advance notice.
Limit disclosure: Share only the portion that the law requires.
Cooperate: Support protective orders, court steps, and reasonable response work.
Related Article: Essential Elements of a Confidentiality Agreement Explained
Set Duration, Return Duties, and Remedies
Confidentiality periods should match the information and relationship. A short project may need a shorter fixed term. Trade secrets may need protection while they remain legally protectable.
Return duties should cover more than paper files. Consider devices, downloads, backups, archives, notes, and derivative materials. Add a written certification when confirmation matters.
Breach remedies should be clear and practical. They may include notice, court orders, damages, fees, or indemnification. Local law may limit some remedies.
Match Duration to Information Sensitivity
Transaction reviews may need protection for a defined period. Customer, pricing, and business information may need longer protection. Trade secrets may require long-term confidentiality obligations.
Avoid careless “forever” language. Tie continuing duties to information that remains a trade secret. Separate fixed duties from obligations that survive the agreement’s end.
Review industry and legal needs before setting a term. Some relationships involve continuing access. Others end quickly after a decision or project.
Require Return or Destruction
Set a clear return or destruction deadline. Identify physical documents, electronic files, copies, notes, and derived materials. Address information stored in shared systems.
Routine backups may need a limited exception. Legal records may also require retention. Any retained copy should remain protected under the NDA.
Ask for written certification when risk justifies it. The certification should identify completed steps. It should also explain any permitted retention.
Specify Practical Breach Remedies
Require prompt notice of a suspected breach. The parties should preserve evidence and investigate the event. They should also limit further access quickly.
Injunctive relief may help stop continuing misuse. This means a court order requiring someone to stop specific conduct. Damages may address proven financial harm.
Indemnification or attorneys’ fees may fit some deals. Use these terms carefully and check governing law. Remedies should reflect realistic risks and actual contract duties.
Information type | Typical protection approach | Return or destruction | Breach response |
|---|---|---|---|
Deal evaluation data | Fixed term tied to the review | Return after the decision | Notice, investigation, and suitable damages |
Customer and pricing data | Longer fixed term | Remove copies after the relationship | Access cutoff and court relief where suitable |
Technical product data | Term linked to project and market risk | Return files, samples, and notes | Investigation, relief, and documented loss |
Trade secrets | Protection while legally protectable | Remove active copies and restrict retained backups | Urgent action, evidence preservation, and remedies |
Related Article: What Happens If You Break an NDA? Understand the Impact
Strengthen Trade Secret Protection Beyond the NDA
An NDA alone does not protect every trade secret. Companies also need reasonable protective measures. Courts may examine how the business handles sensitive information in practice.
Use limited access, secure systems, staff training, and vendor controls. Separate trade secrets from general business information. These steps reduce exposure and support the company’s legal position.
Protection should continue after signing. Review controls when staff, systems, vendors, or products change. A strong program connects contract terms with daily work.
Classify and Segment Sensitive Information
Create clear information levels. A simple model may separate public, internal, confidential, and restricted information. Mark trade secrets as restricted when appropriate.
Use role-based access for sensitive systems. Store trade secrets in controlled repositories. Limit downloads and remove access that people no longer need.
Separate trade secrets from ordinary confidential information. This helps teams apply stronger safeguards. It also makes the scope of custom NDA clauses clearer.
Train Employees and Representatives
Train employees during onboarding. Explain what information is protected and how people may use it. Give clear examples from their daily work.
Repeat training when roles or systems change. Contractors and vendors should receive suitable instructions. Keep records of attendance, acknowledgments, and policy acceptance.
Use exit procedures for departing workers. Collect devices and remove system access promptly. Remind departing staff about continuing employee confidentiality agreements.
Monitor and Review Protection Measures
Review access rights on a regular schedule. Remove access after transfers, project completion, or departure. Audit logs can show unusual downloads or access patterns.
Test incident response steps before a real event. Check whether teams know who must receive notice. Review whether vendors follow agreed security duties.
Update controls when business needs change. New systems, suppliers, products, and markets create new risks. Contract terms should change with those risks.
Adapt Controls to the Industry
Healthcare teams may handle patient information and research data. Finance teams may protect models, forecasts, and client details. Software teams may need strong source code and development controls.
Manufacturers may protect designs, processes, and supplier terms. Research groups may protect formulas, test results, and lab records. Professional firms may protect client work and internal methods.
Industry-specific NDA examples can help teams spot common risks. They cannot replace legal and security review. Each agreement still needs facts from the actual relationship.
Classify: Mark information by risk and identify trade secrets clearly.
Restrict access: Use roles, secure repositories, limited downloads, and regular access reviews.
Train people: Teach employees, contractors, vendors, and advisers how to protect information.
Monitor use: Review logs, test response plans, and investigate unusual activity.
Offboard users: Remove access, recover devices, and repeat continuing confidentiality duties.
Review vendors: Check supplier controls, subcontractors, and ongoing access needs.
Related Article: NDAs (Non-Disclosure Agreements): A guide to secrecy
Improve Enforceability Through Execution and Management
Good language can fail when teams execute it poorly. Correct party names, authority, dates, and signatures matter. So do governing law, dispute terms, and complete document records.
Use consistent best NDA templates for businesses, but control every version. A template should support review, not replace it. Legal teams must approve changes that affect risk.
NDA management software can help track duties after signing. It can reduce missed reviews and lost documents. It cannot replace legal judgment for unusual or high-risk disclosures.
Align Governing Law and Dispute Procedures
Choose governing law that fits the parties and deal. Set a clear court location or arbitration process. Mediation may provide a useful first step for business disputes.
Consider emergency relief for urgent misuse. Cross-border deals need careful review of local rules. Courts may treat signatures, remedies, and data duties differently.
Make the dispute process easy to find. Conflicting venue and arbitration terms create uncertainty. Clear drafting helps the parties act quickly.
Complete Proper Execution
Use the correct legal names for every party. Confirm that each signer has authority. Add dates, signature blocks, exhibits, and approved schedules.
Electronic signatures may support efficient execution. Store the final signed version with its audit record. Send each party the same complete document.
Check that the signed version matches the approved draft. Unsigned exhibits can create uncertainty. Inconsistent names or missing pages can weaken enforcement.
Maintain the Agreement After Signing
Track disclosures, approved recipients, renewals, and return deadlines. Schedule access reviews for long projects. Record amendments and updated contact details.
Use a central record for employees, vendors, and partners. Keep the signed agreement with related disclosure records. This creates a clear audit trail.
NDA management software can send reminders before important dates. It can also support searches across agreements. Teams still need people to review alerts and make decisions.
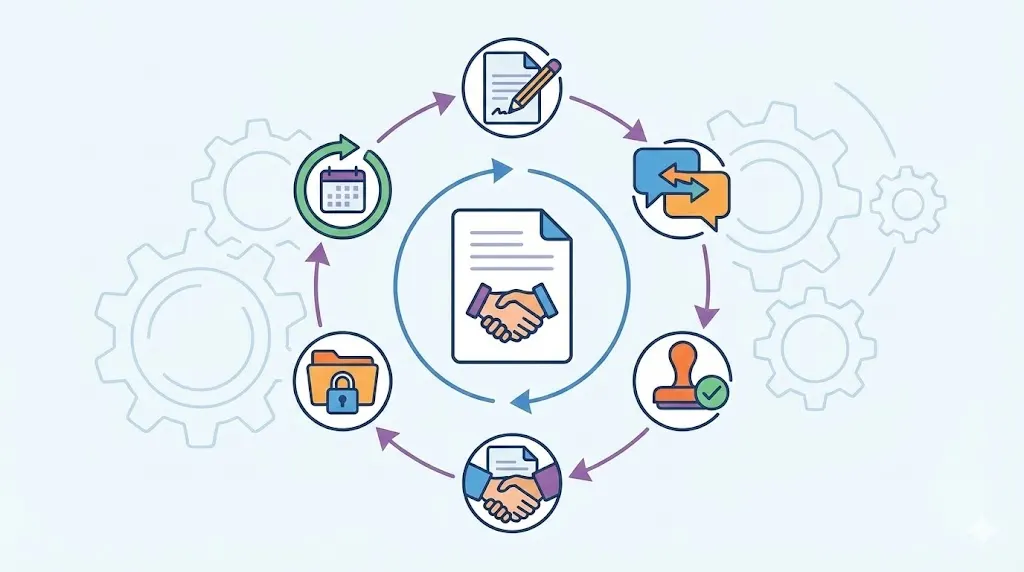
Approve: Confirm the business purpose, risk level, template, and required legal review.
Sign: Verify party names, authority, dates, signatures, exhibits, and final delivery.
Store: Save the signed agreement, version history, and audit record centrally.
Track: Record disclosures, recipients, access reviews, renewals, and return deadlines.
Offboard: Remove access, recover materials, confirm destruction, and preserve allowed records.
Close: Record completion, unresolved duties, amendments, and continuing obligations.
Related Article: How to Protect Sensitive Contracts: Best Practices
Why Contract Management Software Matters
Centralized NDA management software keeps agreements, templates, and records together. Legal teams can manage approvals and signatures from one controlled workspace. Business teams can find current documents without searching old email threads.
Workflow automation can route drafts to the right reviewers. It can send reminders for renewals and return duties. Searchable records can show access history, disclosure details, and confidentiality periods.
This process supports consistent controls across employees, vendors, and partners. It also preserves human review for high-risk disclosures. A clear system helps teams act before an obligation expires.
Volody’s CLM Software supports contract review, contract summaries, and obligation management. It can flag risky language during review. It can also highlight renewal dates, key duties, and contract risks.
For example, a legal team can review a vendor NDA, spot unusual clauses, and track return duties. The team can then monitor renewal dates from one central record.
Want to see how contract management software can simplify your legal workflows? Check out Volody's CLM Software.
FAQ
What is a Non-Disclosure Agreement (NDA)?
An NDA is a legally binding contract that limits confidential information use and disclosure. It identifies the parties, protected information, permitted purpose, and recipient duties. It may also set a confidentiality period and breach remedies. An NDA works best when its language matches the real information, relationship, and business risk.
How should confidential information be defined in an NDA?
Define confidential information with clear categories and examples. Cover business plans, customer lists, pricing, financial data, source code, and trade secrets. Address written, oral, electronic, visual, and physical disclosures. Also state the permitted purpose and labeling process, while avoiding vague terms that create uncertainty.
How long should confidentiality obligations last?
The right period depends on the information, relationship, industry, and applicable law. Transaction reviews may use a fixed period after discussions end. Customer, pricing, and technical information may need longer protection. Trade secrets may require continuing duties while they remain legally protectable.
What information is typically excluded from an NDA?
Common exclusions cover public information, prior knowledge, independent development, and lawful third-party receipt. Information approved for release may also fall outside the agreement. The receiving party should provide proof for these claims. The NDA should also respect protected reporting and required regulatory disclosures.
What obligations should the receiving party have to protect information?
The recipient should limit access to people with a genuine business need. It should use information only for the permitted purpose. The agreement should cover representatives, copying, storage, security controls, and incident notice. It should also require secure return or destruction when the relationship ends.
Can an NDA protect trade secrets by itself?
An NDA is only one part of trade secret protection. Businesses should also use access controls, information classification, secure systems, staff training, and monitoring. Vendor rules and offboarding steps also matter. These practices help prevent misuse and show that the company treated the information as secret.
What happens if someone breaches an NDA?
A breach should trigger prompt investigation, evidence preservation, access restrictions, and required notice. The parties may seek urgent court relief, damages, fees, or indemnification when the agreement and applicable law permit. Complete disclosure and access records provide the foundation for establishing what occurred and assessing the resulting harm.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.


" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)