
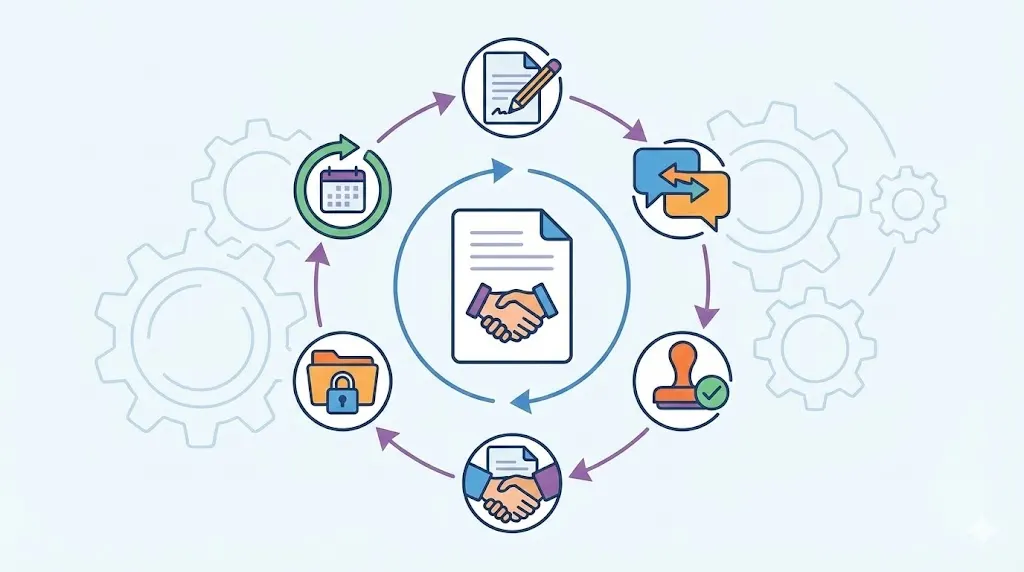
A contract audit trail provides a defensible, chronological record of every agreement-related action. By connecting people, decisions, approvals, signatures, timestamps, and document versions, it gives businesses the evidence they need to strengthen controls, resolve disputes, and maintain audit readiness.
TL;DR
A contract audit trail records access, edits, approvals, signatures, and status changes in a trusted timeline.
Core records include users, roles, timestamps, changes, reasons, versions, permissions, approvals, and signatures.
Common gaps include missing events, weak permissions, mixed timestamps, disconnected systems, and poor record protection.
Strong controls define logged events, assign ownership, protect records, and test audit data often.
Audit trails support procurement, human resources, sales, real estate, education, construction, film, and finance teams.
Contract management software centralizes evidence, automates workflows, improves reporting, and strengthens audit readiness.
What a Contract Audit Trail Captures
Definition and purpose
A contract audit trail is a chronological record of contract activity. It should show who acted, what changed, and when it happened.
The record begins before signature. It can include intake, drafting, negotiation, review, approval, execution, renewal, amendment, and termination.
A reliable trail supports accountability because each action has an owner. It also supports transparency when teams need to explain a contract decision.
The record should resist hidden changes. Secure storage helps preserve trust in Contract Audit Records during reviews.
A complete trail can support compliance audits and legal disputes. It can show the facts without relying on memory.
Basic document storage only preserves files. It does not explain who opened a file or approved a change.
How Audit Trails Differ from Version History
Version history shows how a file changed between saved copies. It may show edited text, file names, and revision dates.
A Contract Document Audit Trail covers much more activity. It can record views, downloads, comments, approvals, signatures, access rights, and workflow changes.
Version control answers a narrow question. It shows which document version existed at a certain point.
An audit trail answers a wider question. It shows how people handled the agreement across its full lifecycle.
For example, version history may show a changed payment term. The audit trail may show the editor, reviewer, approver, reason, and approval date.
This distinction matters during disputes. A business may need proof of actions around a change, not only proof of the change itself.
The Contract Lifecycle Record
The trail should start when a business requests a contract. Intake records can show the requestor, business purpose, owner, and required approval path.
During drafting, it should capture templates, clause changes, comments, and related attachments. During negotiation, it should preserve offers, counteroffers, and review steps.
Approval records should show the assigned approver and decision. Contract Approval Records should also show rejected requests, returned drafts, and approval conditions.
Execution records should include signature events and the final signed version. Later events may include amendments, renewals, notices, obligations, and termination.
A strong Contract Audit History keeps these events connected. It links each event to the right contract, version, party, and workflow.
Related articles: What is Contract Tracking? Your Guide to Contract Monitoring
Essential Data Businesses Need to Record
User Identity, Roles, and Permissions
Every event should identify the person or system that performed it. Names alone may not provide enough context for a useful record.
The event should also show the person’s role and department. It may need to identify an outside counsel, supplier, customer, or signing party.
Permissions matter because access affects the meaning of an action. A reviewer with view access differs from an administrator with editing rights.
The record should capture permission changes as well. This includes new access, removed access, shared links, and changes to approval authority.
Shared accounts weaken Contract Audit Records. They make it harder to prove which person viewed, changed, or approved an agreement.
Businesses should use named accounts and strong identity checks. These controls create clearer ownership for each activity.
Timestamps, Actions, and Context
Each event needs a precise timestamp. The system should record the time zone or convert events into one standard time.
An event also needs a clear activity type. Examples include opened, downloaded, edited, commented, approved, rejected, signed, shared, or archived.
The record should identify the document or clause involved. This detail helps reviewers find the exact text behind a decision.
Context can include the workflow stage, business unit, location, and related request. It may also include the reason for a significant change.
A useful record connects the action to a document version. It should preserve both the prior value and the new value when fields change.
Businesses can use this simple capture checklist:
Identity: Record the user, role, department, and outside party.
Time: Store the exact event time and the system time zone.
Action: Describe the activity using a clear, standard event name.
Document: Link the event to a contract, clause, version, or attachment.
Reason: Capture the reason for material edits, exceptions, or rejected steps.
Status: Record approval, signature, renewal, amendment, and termination status.
Access: Show the device, location, permission, download, share, or access path.
Related articles: Types of Contracts Every Business Needs
4 Key Challenges in Maintaining a Contract Audit Trail
1. Incomplete or Inconsistent Activity Records
A missing view or approval can break the contract story. Reviewers may see the final file without seeing the steps behind it.
Manual notes often miss comments, access events, and rejected requests. Email chains may hold evidence, but they can become difficult to search.
These gaps weaken compliance evidence. They also make disputes harder because teams must rebuild events from memory.
A complete record needs standard event rules. Every contract should produce the same core records at each workflow stage.
2. Unclear Access and Permission Controls
Excessive access creates risk before anyone changes a document. Users may download, share, or edit files without a clear business need.
Shared accounts create another problem. They hide the actual person behind an event.
Poor separation of duties can also weaken approval controls. One person should not always create, approve, and execute the same agreement.
Permission reviews should happen on a regular schedule. They should also happen when people change roles or leave the business.
3. Unreliable Timestamps and Disconnected Systems
Different tools may record events in different time zones. Manual entries may also use unclear or missing dates.
Disconnected systems create duplicate or missing records. A contract may move through email, shared drives, e-signature tools, and business systems.
Without linked identifiers, teams may struggle to match those events. This weakens the Contract Approval Records and the wider Contract Audit History.
A shared time standard helps resolve date conflicts. System links and event IDs can also connect records across tools.
4. Preserving Trustworthy Historical Evidence
Historical records must show what existed at each point. Overwriting old values removes evidence that may matter later.
Tamper-resistant storage helps protect records from silent changes. Immutable storage goes further by preventing later edits to stored events.
Retention controls also matter. Businesses need clear rules for archiving, deletion, legal holds, and approved exports.
Amendments should link to the agreement they change. Superseded versions should remain visible, while the active version stays clear.
The risks follow a simple sequence:
Missing event: The business cannot prove what happened.
Weak permission: An unauthorized user may change or share records.
Mixed timestamp: Reviewers may misunderstand the order of events.
Disconnected system: Evidence may remain outside the main contract file.
Altered history: A dispute may challenge the record’s credibility.
Related articles: Contract Process KPIs That Boost Business Performance
Best Practices for Building a Reliable Audit Trail
Standardizing the Events That Must Be Logged
Start with a written event policy. Define what every contract system must record from intake through termination.
Include document creation, access, edits, comments, reviews, approvals, and signatures. Add status changes, amendments, renewals, notices, and archived files.
Use standard names for events. “Approved” should mean the same thing across departments and contract types.
Clause-level changes deserve special care. The record should show the old language, new language, editor, and reason.
The policy should also cover attachments. A missing schedule or exhibit can change the meaning of the agreement.
Assigning Roles and Approval Responsibilities
Role-based access limits activity to approved users. It also makes each action easier to assign and review.
Approval routing should reflect delegated authority. A low-value purchase may need one approval, while a major deal needs several.
Separation of duties reduces hidden risk. Different people should create, review, approve, and sign when practical.
The process should define backup approvers. It should also record delegated approvals and the dates they apply.
Owners need clear duties after signature. They should review renewals, obligations, exceptions, and unresolved contract issues.
Protecting Records and Controlling Retention
Use secure storage with restricted deletion rights. Encryption protects records while stored and while moving between systems.
Backups should preserve audit data, not only contract files. Recovery tests can show whether the business can restore complete records.
Retention rules should match legal, business, and contract needs. They should define archive dates, deletion steps, and legal hold actions.
Exports should preserve context. A downloaded record should include event details, user data, timestamps, and links to related versions.
A practical rollout sequence looks like this:
Define: Set required events, fields, roles, and retention rules.
Configure: Apply access controls, workflows, time settings, and record formats.
Test: Create sample contracts and check every expected event.
Monitor: Review missing records, unusual access, failed steps, and delays.
Review: Test reports, exports, backups, and permission assignments.
Improve: Fix gaps, update policies, and retrain users after changes.
Related articles: Contract Versions: A Guide to Easily Tracking Each Update
How Audit Trails Support Different Business Functions
Procurement and Vendor Management
Procurement teams need evidence for supplier selection and contract approval. Records may show reviews, bids, pricing changes, and negotiated service levels.
The trail can connect purchase terms with supplier obligations. It can also show who accepted exceptions or changed payment terms.
Vendor managers can track renewal decisions and performance issues. They can review whether required certificates, notices, or approvals were completed.
This evidence supports supplier reviews and payment checks. It can also help teams explain why one vendor received different terms.
Human Resources and Sales
Human resources teams can track policy delivery and employee signatures. The record can show when a person received, viewed, and signed an agreement.
Sales teams need proof around customer contracts. They may track sending, viewing, approval, execution, amendments, and renewal discussions.
Real estate teams can preserve lease approvals, amendments, notices, and access rights. Education teams can track grants, service contracts, and required sign-offs.
Construction teams can record change orders, site approvals, and subcontractor obligations. Film production teams can track talent releases, location agreements, and payment changes.
Financial services teams need clear records for approvals and customer terms. These Contract Audit Records can support reviews of access, exceptions, and control steps.
Related articles: How to Manage Risk Effectively with Contract Management
Using Audit Trails for Compliance, Risk, and Disputes
Preparing for Internal and External Audits
Auditors need more than the final signed contract. They often need proof that the right people reviewed and approved it.
A searchable trail can show the approval path and decision dates. It can also identify the authoritative version used for signature.
Teams can test whether required steps occurred. They can find missing approvals, late reviews, or policy exceptions before an audit begins.
Filterable reports make this work faster. Users can search by contract, owner, department, activity, user, or time period.
Investigating Contract Disputes
A dispute may involve a changed clause or unclear approval. The audit trail can show when the change occurred and who handled it.
Negotiation records may reveal the order of offers and counteroffers. Review comments can explain why one term replaced another.
Signature records can confirm execution timing. Version links can show which document each party reviewed.
This chronology supports fact-based discussion. It does not decide the dispute by itself, but it reduces guesswork.
Managing Financial and Operational Risk
Audit data can reveal weak approval controls. It can also show missed renewals, unassigned obligations, and unusual contract access.
Risk teams can connect contract events with supplier exposure. They can review price changes, service failures, and exceptions across agreements.
Renewal alerts can reduce accidental extensions. Ownership records can show who must act before a notice or deadline.
A Contract Compliance Audit can also test policy rules. For example, a team may check whether high-risk agreements received legal review.
Turning Records into Actionable Reporting
Reports should answer clear management questions. They should show what needs attention, who owns it, and when action is due.
Useful reports can highlight overdue approvals and missing signatures. They can also show unusual access, repeated exceptions, and workflow bottlenecks.
Dashboards should support filters and drill-down views. A manager should move from a summary issue to the related contract events.
Scenario-based evidence mapping makes reporting practical:
Internal audit: Use approvals, permissions, versions, timestamps, and policy exceptions.
Dispute review: Use negotiation history, clause changes, signatures, and final versions.
Security review: Use access, downloads, sharing, permission changes, and unusual activity.
Risk review: Use renewals, owners, obligations, exceptions, and approval failures.
Related articles: Advanced Contract Search for Faster Retrieval
Implementing Contract Audit Trail Controls Across the Business
Start with high-risk agreements and critical business processes. These may include major suppliers, customer deals, employment contracts, leases, and regulated services.
Map the current workflow before buying or configuring tools. Mark every handoff between legal, procurement, finance, sales, business teams, and signers.
Identify where records now live. Common locations include email, shared drives, document tools, e-signature platforms, procurement systems, and customer relationship systems.
Define ownership for each record type. Legal may own templates, while procurement owns supplier approvals and finance owns payment terms.
Set measurable control requirements. Examples include complete event capture, named users, standard timestamps, protected storage, and searchable reports.
Connect systems through stable contract identifiers. This helps link CLM records with identity systems, e-signature tools, enterprise resource planning systems, and customer systems.
Use a phased rollout plan:
Discovery: Map contracts, workflows, systems, risks, owners, and current record gaps.
Policy design: Define events, fields, permissions, retention, reviews, and escalation paths.
Configuration: Set workflows, roles, reports, alerts, timestamps, and storage controls.
Pilot testing: Test selected agreements across departments and connected systems.
User training: Teach staff how to review, approve, change, sign, and share contracts.
Monitoring: Check completeness, access patterns, delays, exceptions, and failed integrations.
Continuous improvement: Update rules, fix gaps, retest controls, and review new risks.
Testing should include real business scenarios. Create an amendment, reject an approval, change a permission, and complete a signature.
Then check the resulting records. They should remain complete, searchable, linked, and protected.
Related articles: How Contracts Strengthen Business Partnerships
Why Contract Management Software Matters
Contract management software brings agreements and workflows into one controlled workspace. It can record drafting, review, approval, signature, renewal, amendment, and termination events.
This reduces reliance on scattered email and manual notes. It also gives teams one place to search Contract Audit History.
Role-based access limits who can view or change each record. Standard workflows reduce skipped approvals and inconsistent Contract Approval Records.
Alerts can flag overdue steps and upcoming renewals. Reports can show missing signatures, unusual access, and repeated workflow delays.
Centralized evidence: A shared repository links contracts, versions, attachments, and activity records.
Users can search by contract, person, date, status, or business unit. This helps auditors find evidence without asking several teams. It also reduces duplicate copies and unclear document ownership.
Controlled workflows: Automated routing sends contracts to the right reviewers and approvers.
Reminders reduce stalled requests and forgotten approval steps. The system records decisions, returns, exceptions, and delegation. This creates a clearer audit trail than informal email approval.
Risk visibility: Reports connect contract events with owners, obligations, access, and deadlines.
Teams can spot unusual activity before it becomes a wider problem. They can also review renewal exposure and missing controls. Better visibility supports faster and more consistent risk decisions.
Volody CLM Software supports this work with AI Contract Review, AI Contract Summaries, and Approval Workflow Automation. AI Contract Review can flag risky clauses and missing terms. AI Contract Summaries can highlight obligations, renewal dates, and key risks. Approval Workflow Automation can route requests, record decisions, and send reminders.
For example, a procurement team can review a supplier contract, route it for approval, and track renewal duties in one place. The resulting records show the changes, decisions, owners, and dates tied to that agreement.
Want to see how contract management software can simplify your legal workflows? Check out Volody's CLM Software.
FAQ
What is a contract audit trail?
A contract audit trail is a chronological record of an agreement’s activity. It can capture creation, negotiation, access, edits, approvals, signatures, amendments, renewals, and termination. Each event should connect to a user, role, timestamp, document version, or workflow step. This helps businesses verify decisions, support audits, and resolve contract disputes.
What distinguishes a contract audit log from an audit trail?
A contract audit log usually means one recorded event, such as a document view or approval. A contract audit trail is the wider timeline built from those events and related evidence. The terms often overlap in practice. The word trail highlights the full contract history and the links between actions.
How do audit logs differ from audit trails and system logs?
An audit log records separate events created by a system. An audit trail organizes relevant events into a clear history of one contract or process. A system log captures broader technical activity, such as errors or server access. Contract trails focus on accountability, control checks, compliance, and business decisions.
What should businesses record in a contract audit trail?
Businesses should record users, roles, timestamps, activity types, document versions, and affected clauses. They should also capture original and changed values, reasons, approvals, signatures, access, downloads, sharing, and permission changes. Attachments, amendments, renewals, and workflow status also matter. These records make audits and dispute reviews more reliable.
How long should businesses keep contract audit trail records?
Retention should follow applicable laws, contracts, business rules, and dispute risks. Teams should consider the agreement type, industry, location, tax needs, and legal holds. The policy should define archive and deletion steps. It should also preserve relevant evidence when a dispute, investigation, or legal hold begins.
How can businesses protect contract audit trail data?
Businesses can protect contract audit trail data with named accounts, role-based access, encryption, secure backups, and tamper-resistant storage. Regular permission reviews and monitoring for unusual downloads, sharing, and access further strengthen controls. Restrict deletion, preserve timestamps across connected systems, and ensure controlled exports retain event details and chain of custody. For a more reliable implementation, evaluate contract management software that centralizes and protects these records.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.
" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)