

A well-drafted NDA establishes clear, enforceable rules before sensitive business information changes hands. It defines how information may be accessed, used, stored, and disclosed while aligning protection with the deal, the information, and the people involved. Strong drafting gives businesses greater clarity, control, and confidence throughout the relationship.
TL;DR
An NDA protects defined business information and sets rules for sharing, use, storage, and disclosure.
Vague terms, broad restrictions, and weak exceptions can make confidentiality duties hard to enforce.
Strong NDAs cover purpose, parties, permitted use, exclusions, duration, return duties, and breach remedies.
Match protection to trade secrets, customer data, source code, pricing, financial records, and deal materials.
Practical controls, legal review, and regular updates support confidentiality after signing.
Contract management software helps teams draft, approve, store, monitor, and renew NDA contracts.
What an NDA Protects and When to Use One
An NDA, or non-disclosure agreement, is a contract. It limits how one party may use or share defined information. The agreement protects information that gives a business value or advantage.
Confidential Information in a Business Context
Confidential information can include trade secrets, product plans, and pricing. It can also include customer data, financial records, source code, and technical designs.
The business context shapes what deserves protection. A restaurant may protect a recipe and supplier pricing. A software company may protect source code, product plans, and system designs.
The NDA should explain these categories in plain terms. It should also cover information that a reasonable person would understand as private. This matters when documents lack a confidentiality label.
A business must also protect information in practice. Need-to-know access, secure storage, and staff training support the contract. Courts may view these steps when assessing whether information received real protection.
How Unilateral and Mutual NDAs Differ
A unilateral NDA protects information shared by one party. This structure suits a company sharing plans with a contractor or investor. The recipient carries the main confidentiality duties.
A mutual NDA protects information shared by both parties. Businesses often use this form during partnerships, joint projects, or acquisition talks. Each side may then act as both discloser and recipient.
The choice depends on the expected information flow. Do not use a mutual form simply because it looks fairer. A wider form may create duties that the business does not need.
When drafting a mutual NDA, define each party’s role clearly. State whether the same rules apply to both sides. Also check whether each party needs the same exceptions, term, and remedies.
Situations That Call for an NDA
Businesses often use NDAs before sharing sensitive information. Common settings include hiring, vendor work, investment talks, and product testing.
An NDA may support discussions with a potential buyer. It may also cover due diligence during an acquisition. Strategic partners may need access to plans, forecasts, or customer details.
Employees and contractors may receive confidential information every day. Employment terms can include confidentiality duties, but a separate NDA may add useful detail.
The agreement should support a defined purpose. It should not replace access controls, secure systems, or staff training. A contract cannot protect information that a business shares without care.
Related Article: Best Word Add Ins To Automate Legal Document Drafting
Key Challenges That Can Weaken an NDA
A strong NDA must protect real interests without creating impossible duties. Poor drafting can create disputes before any breach occurs. The following challenges often weaken confidentiality protection.
Defining the information: Vague wording can cover almost anything. That approach may confuse the recipient and invite later disputes. Describe categories linked to the business purpose and planned disclosure. Include oral discussions when the parties may share information in meetings.
Avoiding excessive scope: An NDA should not block lawful work or ordinary business activity. Broad wording may reach public knowledge or independent ideas. Limit use, not legitimate competition, unless another valid agreement applies. Keep the restrictions tied to the shared information and stated purpose.
Writing usable duties: Recipients need clear rules for access, storage, and sharing. A duty to protect information “at all times” may lack practical meaning. State who may access the material and why. Require reasonable care that matches the information’s sensitivity.
Handling disclosure exceptions: Some information may already be public or independently known. Other material may come from a lawful third party. A subpoena or law may also require disclosure. The NDA should require prompt notice when notice is legally allowed.
Supporting the contract: Contract terms work best with daily controls. Limit access to people who need the information. Train staff, secure files, and track approved sharing. Prepare an incident plan before a suspected leak occurs.
These steps make confidentiality duties easier to follow. They also give the disclosing party better evidence after a problem.
Related Article: How Agentic AI Is Transforming In House Legal
Essential Clauses for a Strong NDA
A non disclosure agreement template can save time during routine deals. It should still receive review before use. A template must reflect the parties, purpose, law, and information involved.
Identifying the Parties and Permitted Purpose
Name each party using its full legal name. Check its address, entity type, and signing authority. A wrong party name can complicate enforcement later.
Identify affiliates and representatives when they may receive information. Representatives may include employees, lawyers, accountants, lenders, and contractors. State whether the main recipient remains responsible for their conduct.
The purpose clause should explain why the information is shared. For example, the purpose may involve reviewing a partnership or testing software. A clear purpose limits later use and guides interpretation.
Avoid a purpose that says “any business matter.” That phrase gives little useful direction. Tie the purpose to a project, transaction, service, or evaluation.
Defining Information, Obligations, and Exclusions
Define confidential information by category and context. Include written, electronic, visual, and oral information where needed. Marked documents should receive protection, but markings should not control everything.
The recipient should use information only for the stated purpose. It should share information only with approved representatives. Those representatives should face duties at least as protective as the NDA.
The NDA should require reasonable care and suitable security. It may require password controls, limited downloads, or secure file transfer. Choose controls that fit the information and the relationship.
Standard exclusions keep the agreement fair. They often cover information that becomes public without breach. They may also cover prior knowledge, independent development, and lawful receipt from another source.
The agreement should address proof for each exclusion. The recipient may need written records showing prior knowledge or independent development. Clear proof rules can reduce arguments after a dispute begins.
Setting Duration, Return, and Remedies
Separate the NDA term from the confidentiality survival period. The term controls when the parties may share information. The survival period controls duties after sharing ends.
Set a period that matches the information’s useful life. Product plans may lose value after launch. Trade secrets may need protection while they remain secret.
Return or destruction terms should cover copies and extracts. They should address backups, legal records, and routine archives. A recipient may need to keep some records under law or policy.
The NDA can require written confirmation of destruction. It can also require prompt notice after unauthorized access. Early notice gives the owner time to contain the harm.
Remedies may include monetary damages or injunctive relief. Injunctive relief asks a court to order conduct, such as stopping disclosure. Attorneys’ fees may apply where the contract and law allow them.
No remedy is automatic. The facts, agreement, and governing law control the result. Draft remedies with care, especially where trade secrets or customer data face exposure.
Related Article: Procurement Contract Risks That Could Sink Your Business
Tailoring Protection to the Information You Share
An NDA should match the information’s format, value, and risk. A source code file needs different controls than a public sales deck. Customer records may also trigger privacy duties beyond the NDA.
Use a classification matrix before sharing sensitive material. This helps teams choose access rules and handling steps. It also makes the NDA more useful during daily work.
Trade secrets: Limit access to named teams and approved advisors. Mark files clearly and store them in controlled systems. Share only the material needed for the stated purpose. Retain records that show secrecy measures and approved access.
Source code and technical designs: Use secure repositories with download controls. Prevent broad copying, personal storage, and unapproved device access. Require return or deletion when testing ends. Keep access logs for code, designs, and technical notes.
Customer and personal data: Share the smallest useful data set. Use secure transfer methods and limit access by role. Apply privacy rules that govern collection, use, and retention. Add prompt notice duties for suspected loss or exposure.
Pricing and financial records: Restrict access to deal teams and approved advisors. Mark forecasts, margins, and price lists as confidential. Avoid sharing more detail than the business purpose requires. Set retention rules for copies, exports, and working papers.
Acquisition and strategy materials: Control access through a data room or similar system. Record who receives plans, forecasts, and diligence files. Limit use to the proposed transaction. Remove access when talks end or the deal changes.
The matrix should guide the contract and operations. It should not create rules that staff cannot follow. Review classifications when projects, systems, or relationships change.
Related Article: Effectively Use AI in Contract Drafting
Making Confidentiality Duties Practical to Operate
A signed NDA does not show who accessed a file yesterday. It also cannot stop every careless email or download. Businesses need simple controls that connect contract terms with daily work.
Controlling Access and Representatives
Use need-to-know access for confidential material. This means people receive access only when their task requires it. It reduces exposure without stopping useful work.
List the types of representatives who may receive information. Require approval for outside advisors, subcontractors, and vendors. Their contracts should include confidentiality terms that match the main NDA.
The recipient should remain responsible for representative conduct. This creates one clear point of responsibility. It also prevents a party from avoiding duties through an outside service provider.
Security measures should match the risk. Use controlled folders, strong passwords, encryption, and secure transfer tools. For highly sensitive data, restrict downloads and use access logs.
Access should end when the task ends. Remove permissions when staff leave, vendors finish work, or talks stop. Keep records of approvals, changes, and removals.
Responding to Disclosures and Documenting Compliance
The NDA should require prompt notice of suspected disclosure. The notice should state what happened, when it happened, and what information was involved. It should also identify known recipients or systems.
The parties should cooperate on containment and investigation. They may need to secure accounts, recover files, or notify affected people. The agreement should support these steps without delaying urgent action.
Create an internal escalation path for suspected incidents. Tell staff whom to contact and what evidence to preserve. Do not let employees investigate sensitive events without guidance.
Document disclosures, approvals, returns, and destruction actions. Keep the signed NDA with related records and access logs. Good records can support a response and clarify each party’s duties.
Review incidents after containment ends. Identify weak controls, unclear language, or training gaps. Update the NDA process when the same risk may appear again.
Related Article: Contract Permissions: Managing Access with Precision
Remedies and Best Practices for Enforceability
Enforcing non disclosure agreements legally depends on more than strong words. Courts may examine scope, notice, proof, fairness, and local law. A careful process supports the agreement from review through enforcement.
Matching Remedies to the Actual Risk
Remedies should reflect the harm that disclosure may cause. A leaked product idea may require fast action. A minor administrative error may call for correction and deletion.
An injunction may help stop continued use or disclosure. The court decides whether that relief is available. The party seeking it must meet the legal test that applies.
Damages may address financial loss caused by a breach. They can be difficult to prove when information has wide business value. Keep records that show the information’s role, value, and use.
Notice duties support quick action after a suspected breach. The NDA may also require cooperation with containment efforts. These duties should remain practical and clear.
Do not promise remedies that the law may not support. Avoid automatic penalties that lack a clear basis. Ask counsel to review unusual damages clauses and emergency relief terms.
Keeping Terms Reasonable and Specific
Reasonable terms are easier for people to follow. They also give a court clearer boundaries to review. Tie restrictions to the purpose, information, and relationship.
Avoid blocking information that anyone may lawfully use. Do not treat all business knowledge as a trade secret. Separate confidential duties from non-compete or non-solicit restrictions.
Set a duration that reflects the information’s life. Protect trade secrets while they remain secret, where law allows. Use a defined period for other material when indefinite duties serve no clear purpose.
Choose governing law and venue with care. Governing law identifies which rules may apply. Venue identifies where a dispute may be heard.
Dispute terms should fit the transaction and party locations. Arbitration may offer privacy, while court action may support urgent relief. Legal advice can help weigh these choices.
Reviewing the NDA Before and After Signing
Have counsel review material agreements and local legal limits. This matters when the deal crosses states or countries. California and other jurisdictions may restrict overbroad terms.
Confirm each signer has authority to bind the party. Check the final document against the approved version. Store the executed copy where authorized users can find it.
Review the NDA when the relationship changes. A new project may involve different data or representatives. An amendment may be better than relying on an old purpose clause.
Review obligations after the agreement ends. Check return, destruction, access removal, and surviving duties. Execution starts the process; it does not finish it.
Related Article: What Happens If You Break an NDA? Understand the Impact
Building an NDA Process That Scales With the Business
Growing teams often send many NDAs through different channels. That can create duplicate forms, missing signatures, and uncertain dates. A simple process gives teams speed without losing legal control.
Standardizing Templates Without Overreliance
Approved templates help teams begin with known language. Clause libraries can offer tested options for common business needs. They can also support unilateral and mutual NDA structures.
Templates should leave room for transaction details. Users may need to change the purpose, term, representatives, or security duties. A fixed form may fail when the information or risk changes.
Do not reuse an unreviewed form across every relationship. Laws and market practices may differ by location and industry. A vendor NDA may not suit acquisition diligence or employment use.
Set rules for template choice and legal review. Low-risk matters may use an approved form. Sensitive deals should route to counsel before disclosure begins.
Managing Approval, Execution, and Ongoing Obligations
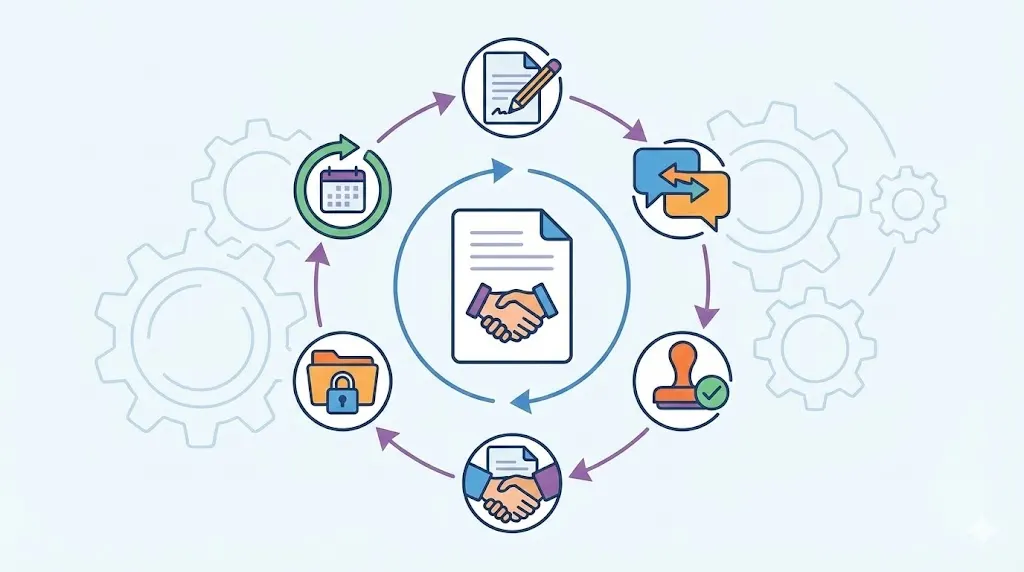
Route each NDA to the right business and legal approvers. Track edits, comments, and approval decisions in one record. This reduces confusion about which version received approval.
Verify signatures and store the final executed document. Make records searchable by party, purpose, date, and project. Link amendments and related agreements to the main NDA.
Track the term and surviving confidentiality duties. Set alerts for expiration, renewal, review, return, and destruction dates. Reminders help teams act before duties become forgotten.
Central oversight also supports vendor and employment records. It can connect NDAs with data processing terms and intellectual property clauses. It can also preserve dispute records and incident actions.
Report on open approvals, upcoming dates, and missing documents. Managers can then see where teams share information without current protection. Legal teams can focus attention on exceptions and higher-risk matters.
Related Article: CLM Software for Compliance & Risk
Why Contract Management Software Matters
Contract management software can help businesses manage NDAs consistently. It does not replace legal judgment or careful drafting. Instead, it connects approved language with controlled business steps.
A central system can hold templates, clause options, and executed agreements. It can preserve version history and show who approved each change. Search tools can help teams find parties, duties, dates, and related records.
Volody’s CLM Software supports NDA work through AI Contract Drafting, Approval Workflow Automation, and a Central Contract Repository. AI Contract Drafting can create first drafts from approved templates and clause libraries. Approval Workflow Automation can route agreements to legal and business reviewers. The repository can store signed NDAs with search and document history.
For example, a company can create a mutual NDA for partner talks. The system can route the draft for approval, store the signed copy, and alert teams about renewal dates. It can also help staff find return or destruction duties later.
Use structured workflows to route NDAs for legal and business approval before disclosure occurs.
Maintain records of executed agreements, parties, obligations, dates, amendments, and related documents.
Connect contract visibility with renewals, returns, destruction duties, and incident response.
Want to see how contract management software can simplify your legal workflows? Check out Volody's CLM Software.
FAQ
What is a non-disclosure agreement (NDA)?
A non-disclosure agreement is a contract that limits use and disclosure of defined information. It identifies the parties, business purpose, and receiving party’s duties. An NDA may protect trade secrets, customer data, financial records, technical material, and product plans. Its strength depends on clear terms and practical protection.
What key elements should an NDA include?
An NDA should identify the parties, purpose, and confidential information. It should explain permitted use, access rights, security duties, exclusions, and legally required disclosures. It should also cover duration, return or destruction, notice, and remedies. The wording should match the transaction and governing law.
When should a business use an NDA?
A business should consider an NDA before sharing sensitive information with outside parties. Common examples include contractors, vendors, investors, buyers, and strategic partners. Employees may also need detailed confidentiality terms. The NDA should support access controls and training, rather than replace them.
How long should confidentiality obligations last?
The NDA term covers the period for sharing information. The survival period covers duties after sharing ends. Other information may need protection for a defined period. Trade secrets may need protection while they remain secret, subject to applicable law and the agreement’s wording.
What exclusions should an NDA contain?
Common exclusions cover public information, prior knowledge, independent development, and lawful third-party receipt. The NDA should also address disclosure required by law, subpoena, or court order. It may require notice when notice is legally allowed. These rules keep the agreement fair and easier to apply.
What is the difference between an NDA and a confidentiality agreement?
An NDA and confidentiality agreement usually serve the same purpose. Both restrict the use and sharing of protected information. Some businesses use the names interchangeably. The actual clauses matter more than the title, especially for purpose, exclusions, duration, and remedies.
What is a mutual NDA?
A mutual NDA protects information shared by both parties. Each party becomes a discloser and recipient under the agreement. This structure suits partnerships, joint projects, and acquisition discussions. The agreement should apply matching duties unless the parties need different rules.
What are the consequences of breaching an NDA?
Protect your business information with a carefully drafted, operationally supported NDA. Engage qualified counsel to review your agreement, then implement the access controls, workflows, and monitoring needed to make confidentiality enforceable in practice.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.


" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)