
Samya Namdeo
An effective NDA protects sensitive information through precise, enforceable obligations tailored to the transaction. Its terms should reflect the parties, the information being shared, the permitted use, and the consequences of misuse. Careful drafting strengthens legal enforceability, reduces operational risk, and supports stronger breach claims. This guide explains how to customize an NDA with clear provisions and practical controls.
TL;DR
Define confidential information clearly, then connect its use to one specific business purpose.
Match exclusions, access rules, duration, and destruction duties to the deal’s real risks.
Add clear remedies, ownership protections, governing law, and required disclosure procedures.
Adapt the NDA for technology, healthcare, finance, employment, and personal data risks.
Review the signed NDA, train users, and track duties as the relationship changes.
Use contract management software to manage approvals, deadlines, versions, and audit records.
Start With the NDA’s Purpose and Risk Profile
Customization should begin with the transaction, not a blank template. First, identify why the parties need to share information.
A buyer may review records during due diligence. A vendor may need access to customer data. An employee may handle trade secrets every day. Each setting creates different threats and duties.
A good risk profile also supports better negotiation. It shows which terms need strong protection and which terms can remain simple. This approach helps avoid an overbroad NDA that may face enforcement problems.
Identify the Parties and Representatives
Use each party’s full legal name and registered address. Do not rely only on brand names, short names, or informal labels.
Define who may receive the information. This group may include employees, officers, contractors, advisers, affiliates, accountants, lenders, and consultants.
The NDA should explain whether representatives act for one party or both parties. It should also state whether the receiving party remains responsible for their conduct.
List relevant affiliates when they may receive information. Otherwise, an affiliate may gain access without clear contractual duties.
Check signer authority before execution. A signed NDA can still create process problems when the wrong person signs it.
Match the NDA to the Business Context
A one-way NDA suits situations where only one party shares sensitive material. This structure often fits employees, contractors, vendors, and potential investors.
A mutual NDA fits relationships where both parties will share protected information. This structure can support joint ventures, partnerships, and acquisition talks.
A customer NDA may need service limits and data controls. An employment NDA may need trade secret, invention, and lawful reporting terms.
A merger review may require clean-team rules. These rules limit sensitive information access to approved people.
Choose a standalone NDA when confidentiality needs broad treatment. Use an embedded clause when confidentiality supports one larger agreement.
Evaluate the Information and Potential Harm
Rank information by sensitivity, value, and likely misuse. Source code and pricing plans may need stronger controls than public brochures.
Consider legal exposure as well. Personal data, health records, and financial information may trigger extra duties.
Ask what happens after a leak. Possible harm includes lost sales, customer claims, regulatory action, and damaged negotiations.
Consider the transaction stage too. Early talks may involve broad business plans. Later diligence may involve detailed records and system access.
Related Article: Drafting Effective NDAs for 2026: A Strategic Guide
Define Confidential Information With Precision
A clear definition helps the receiving party understand its duties. It also gives a court better facts when a dispute arises.
The definition should be broad enough to protect real business interests. It should not cover every fact the receiving party encounters.
Describe the information and its link to the transaction. This approach works better than vague language covering all information “of any kind.”
Describe Covered Information and Formats
List the information types that matter for this deal. Common categories include product plans, pricing, forecasts, customer data, and supplier terms.
Add technical categories when needed. These may include source code, designs, formulas, models, test results, and system diagrams.
Cover different formats clearly. Written, oral, visual, electronic, and recorded information may all require protection.
State how oral disclosures become protected. The NDA may require written confirmation within a set period.
Include copies, notes, extracts, and analyses. Otherwise, protection may not cover materials created from the original information.
Connect Information to the Permitted Purpose
State one clear business purpose for receiving the information. Examples include evaluating a partnership, providing services, or reviewing an acquisition.
Then limit use to that purpose. A party should not use diligence data for sales, hiring, or competitive planning.
Avoid relying on a broad promise to “keep information confidential.” Use restrictions should stand separately from disclosure restrictions.
Vague wording | More useful custom wording |
|---|---|
All information shared by the disclosing party | Product plans, pricing data, customer records, source code, and forecasts shared for the proposed reseller deal |
Information disclosed in any form | Written, oral, visual, electronic, and recorded information connected to the stated project |
Use for any business purpose | Use only to assess and negotiate the proposed services agreement |
Information related to the parties | Information supplied by the named party, its approved affiliates, or listed representatives |
All business information | Information that fits the listed categories or bears a clear confidentiality marking |
Use confidentiality markings when practical. Still, do not let missing labels remove protection from clearly sensitive information.
Related Article: NDAs (Non-Disclosure Agreements): A guide to secrecy
Build Fair Exclusions and Handling Duties
Exclusions keep an NDA balanced and more defensible. They prevent a party from claiming ownership over public or independently created knowledge.
Handling duties turn broad promises into daily actions. They should match the receiving party’s systems, staff, and level of access.
Each exclusion should include a proof rule. The receiving party may need records showing when it learned the information.
State the Core Exclusions
Exclude information that enters the public domain without a breach. Public information should not remain restricted forever.
Exclude information already known without a confidentiality duty. The receiving party should support that claim with dated records.
Exclude information developed independently without using protected material. Keep project records that show separate development work.
Exclude information received lawfully from another source. That source must have the right to share it.
Include disclosures required by law, regulation, subpoena, or court order. The agreement should still limit the disclosure when possible.
Set Use, Access, and Security Controls
Limit access to people who need the information for the permitted purpose. This reduces exposure and supports practical NDA risk management strategies.
Require reasonable safeguards that match the information’s sensitivity. These may include access controls, secure storage, encryption, and staff training.
Address copying, downloading, printing, and sharing. The receiving party should create only necessary copies.
Restrict uploads to personal drives, public tools, and unapproved platforms. This point matters when staff use generative AI or other online systems.
State whether remote access is allowed. Add rules for devices, networks, and records kept outside company systems.
Address Representatives and Third Parties
Define approved representatives by role or relationship. Avoid language that permits unlimited access to unknown third parties.
Require each representative to follow duties at least as strict as the NDA. Written agreements may be useful for contractors and advisers.
Keep the receiving party responsible for representative breaches where appropriate. This creates one clear point of responsibility.
Require notice before sharing information with a new third party. The disclosing party may need to approve certain recipients.
Exclusion or duty | Evidence to keep | Responsible personnel | Useful control |
|---|---|---|---|
Public information | Public page, report, or dated release | Legal or business owner | Review the source date |
Prior knowledge | Earlier files or emails | Receiving team | Preserve dated records |
Independent development | Project notes and code history | Technical lead | Separate workspaces |
Lawful third-party receipt | Source agreement or written confirmation | Legal team | Check sharing rights |
Approved access | User list and access log | System owner | Apply role-based access |
Secure handling | Policy record and training log | Security or compliance team | Use approved systems |
Representative sharing | Approval record and signed duty | Contract owner | Track each recipient |
Related Article: NDA and Confidentiality Agreement : The Ultimate Guide
Set Duration, Return, and Destruction Requirements
Duration should reflect the information’s commercial life. A short-lived sales plan may not need the same term as source code.
Fixed terms can suit general business information. Trade secrets may need protection while they remain secret.
Termination should not end every duty at once. Non-use, ownership, dispute, and remedy terms may continue afterward.
Choose a Defensible Confidentiality Period
Use a fixed period for information with a limited business life. The NDA should state when that period begins.
An event-based term can work when the relationship has no fixed end date. For example, duties may continue after the project ends.
Use separate terms for different information types when needed. General business data may have one term, while trade secrets survive longer.
Perpetual protection should fit information that remains a trade secret. It should not become a default for every business detail.
Check the term against local law and the deal’s facts. An extreme term may appear unfair or harder to enforce.
Define Return and Destruction Procedures
Set a clear deadline for return or destruction. The deadline may begin after a written request or project end.
Cover paper records, electronic files, copies, extracts, notes, and analyses. Include data stored in shared drives and collaboration tools.
Address backups and archives with care. Some records may remain under legal retention duties or normal backup cycles.
Require continued protection for retained records. Retention should not create a new right to use the information.
Ask for written certification when the risk justifies it. The certificate should identify the records covered and the completion date.
Information category | Suggested planning approach | Post-termination action |
|---|---|---|
General business plans | Use a fixed period tied to business value | Return or destroy records after the stated deadline |
Customer and supplier data | Use a term matching contract and privacy duties | Delete, return, or retain only when law requires |
Source code and technical designs | Protect while the information remains sensitive | Remove access and preserve only approved legal records |
Trade secrets | Continue protection while secrecy remains | Restrict access and document approved retention |
Negotiation records | Protect through the deal and dispute period | Archive securely or destroy under the agreed process |
Related Article: How to Draft an Effective Unilateral NDA for Your Needs
Address Remedies, Disputes, and Enforceability
Remedies show how the parties will respond to a breach. They also help allocate risk before problems occur.
NDA legal enforceability depends on clear wording, reasonable limits, and applicable law. Courts may question terms that protect more than the business interest requires.
A remedy clause cannot fix a vague definition. Strong protection starts with clear duties and evidence.
Specify Breach Consequences
State whether the disclosing party may seek injunctive relief. This court order can require a party to stop using or sharing information.
Address monetary damages for proven loss. The clause should avoid promising sums that local law may reject.
Include attorneys’ fees only where permitted. Fee language should also explain when recovery applies.
Use liquidated damages carefully. A preset amount should reflect expected loss, not punish the receiving party.
Consider indemnification for third-party claims where suitable. This may matter when a breach causes customer or regulator action.
State whether remedies are cumulative or limited. Conflicting remedy terms can create uncertainty during enforcement.
Select Governing Law and Dispute Procedures
Choose governing law that connects logically to the parties or transaction. Avoid selecting a forum for convenience alone.
Name the venue and court location. Clear venue terms can reduce early disputes about where claims belong.
Consider mediation or arbitration for suitable relationships. Also preserve emergency court relief when urgent action is needed.
Address cross-border enforcement early. Local rules may affect service, evidence, injunctions, and judgment recognition.
Set notice rules for suspected breaches. Include approved contacts, timing, and required details.
Preserve Intellectual Property Boundaries
State that disclosure transfers no ownership. The receiving party should gain no rights beyond the permitted purpose.
Add a clear no-license clause. It should cover patents, copyrights, trademarks, trade secrets, and other intellectual property.
Address residual knowledge with care. A residuals clause may weaken protection when people retain sensitive ideas after access.
Protect independently developed work when appropriate. Do not block general skills, experience, or lawful work without a clear reason.
Review clauses that conflict with employment laws or trade secret rules. Some laws protect reporting, mobility, or other lawful conduct.
Review area | Key question |
|---|---|
Breach response | Can the owner seek urgent relief after a suspected leak? |
Damages | Are loss rules clear and allowed under applicable law? |
Forum selection | Does the chosen court or process fit the transaction? |
Intellectual property | Does disclosure grant any unintended license or ownership right? |
Duration | Does the term match the information’s real value? |
Drafting risk | Could broad, vague, or conflicting language weaken enforcement? |
Related Article: What Happens If You Break an NDA? Understand the Impact
Tailor Protection to Industry and Transaction Needs
Industry context changes the risks behind an NDA. A general template may miss controls required for technical, personal, or regulated data.
Start by mapping information flows. Find who creates the information, who receives it, and where systems store it.
Industry terms should support real controls. A clause cannot protect data that staff can freely download or share.
Technology and Intellectual Property Transactions
Technology deals often involve source code, models, algorithms, and product roadmaps. These materials can create serious competitive harm after one leak.
Limit access to named teams and approved environments. Do not permit broad access because a person works for the receiving company.
Address credentials, test systems, and security reports. These items can expose live systems or reveal weak points.
Restrict uploads to public tools and external AI services. Cover model training, retention, prompts, outputs, and human review where relevant.
Consider residual knowledge carefully. The receiving party should not use retained technical details outside the agreed purpose.
Regulated Data, Employment, and Contractor Relationships
Personal information may require stronger handling and deletion rules. Health, payment, and identity data may also trigger separate legal duties.
Add breach notification duties that fit the deal. State who receives notice and what early facts the notice should include.
Employment NDAs should protect trade secrets without blocking lawful work. They should also coordinate with invention and confidentiality agreements.
Contractor NDAs should address subcontractors and system access. Confirm that the contractor can meet each security duty in practice.
Finance deals may require records, insider rules, or restricted teams. Healthcare deals may require role limits, audit records, and retention controls.
Context | Information categories | Additional clauses | Review question |
|---|---|---|---|
Software deal | Code, designs, credentials, test data | AI use, access logs, security notice | Who can access technical systems? |
Healthcare project | Patient and clinical records | Privacy, breach notice, deletion | Which records require special handling? |
Finance project | Forecasts, account data, deal terms | Insider controls, restricted access | Which users need separate approval? |
Employment | Trade secrets, plans, inventions | Lawful reporting, work product | Does the NDA fit employment law? |
Contractor work | Customer data, files, system access | Subcontractor and return duties | Can the contractor enforce these controls? |
Related Article: Types of NDA Explained: Choose the Right One for You
Review, Approve, and Maintain the Customized NDA
Signing does not end the NDA process. Teams must still control access, track deadlines, and preserve evidence.
A good process connects legal review with daily work. That connection helps prevent accidental waivers and missed obligations.
Keep the final agreement with related records. Emails, approvals, access lists, and destruction certificates may matter later.
Conduct Legal and Business Review
Ask counsel to review governing law and enforcement risks. Legal review should match the transaction’s value and complexity.
Have the business owner confirm the permitted purpose. The wording should reflect what teams will actually do.
Check the NDA against related agreements. Conflicts may appear in services contracts, employment terms, data agreements, or purchase documents.
Confirm negotiation points before sending the draft. This reduces repeated edits and unclear internal positions.
Use the best NDA templates for businesses as starting points only. Templates save time, but they cannot replace transaction-specific review.
Confirm Operational Readiness
Tell employees and representatives what information they may access. Explain approved systems and sharing channels.
Set an escalation path for suspected disclosure. People should know whom to contact and how quickly.
Train users before access begins. Short, practical guidance often works better than a long policy.
Check whether technical controls match the NDA. A contract may restrict downloads, but systems must enforce that rule.
Document approvals for unusual access. This record can help show consistent NDA risk management strategies.
Manage and Reassess the Agreement
Use one version with a clear effective date. Store signed copies where legal and business teams can find them.
Track renewal dates, confidentiality periods, and destruction deadlines. Also track representative duties and related contracts.
Keep an audit trail for changes and approvals. Do not overwrite earlier versions without preserving history.
Reassess the NDA when the project changes. New parties, data types, systems, or countries may require amendments.
Review the agreement after a suspected incident. Preserve evidence before changing access or deleting records.
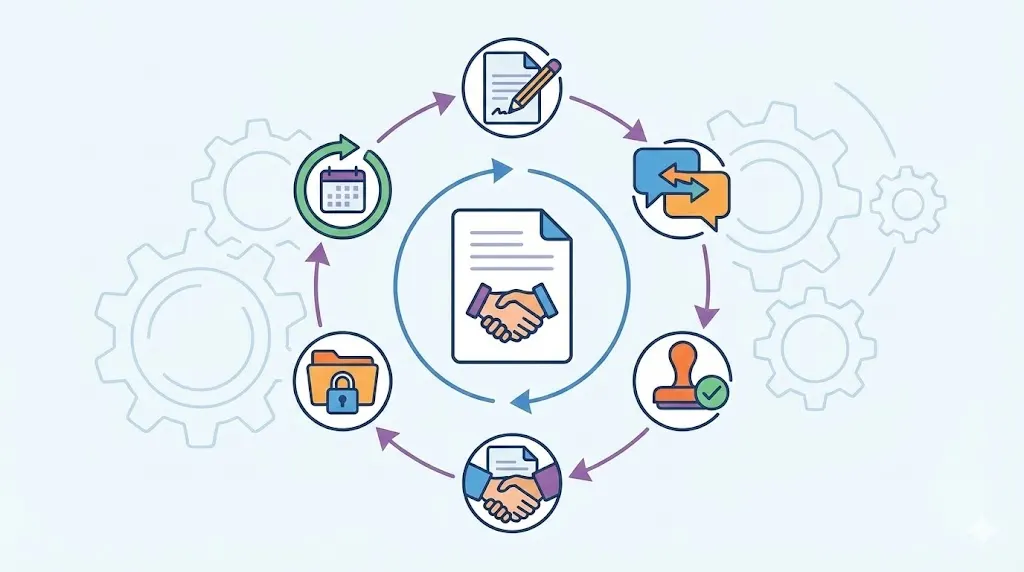
Assess: Identify parties, purpose, information, threats, and transaction stage.
Record the business owner and legal reviewer for each deal. Rank the information by value, sensitivity, and legal exposure. Confirm whether a unilateral or mutual NDA fits the information flow.
Draft: Customize definitions, exclusions, access rules, duration, and remedies.
Add no-license language and clear permitted-use limits. Address AI tools, privacy duties, and required disclosures where relevant. Use plain wording that gives the receiving party fair notice.
Approve: Send the draft through business and legal review.
Confirm signer authority, governing law, and dispute procedures. Compare the NDA with related employment and commercial agreements. Resolve conflicting terms before signature and system access.
Sign: Store the executed copy in a controlled repository.
Record the effective date, parties, term, and approved representatives. Link the NDA to the project, purchase order, or main contract. Restrict access to the final agreement and related records.
Monitor: Track duties, renewals, access changes, and destruction deadlines.
Review whether users follow approved handling and sharing rules. Record incidents, notices, approvals, and completed destruction actions. Update the NDA when the scope or risk profile changes.
Related Article: AI for NDA Review in 2025: Top 3 Tools You Might Want To Try
Why Contract Management Software Matters
Contract management software gives teams a controlled platform for NDA customization. It keeps drafts, approvals, signatures, duties, and deadlines together.
Volody's CLM Software supports a Central Contract Repository with search and OCR. It also offers Approval Workflow Automation and Obligation Management for key duties.
For example, a legal team can route a tailored NDA for approval. The system can then track its term, destruction deadline, and signed version.
Centralize NDA templates, negotiated versions, approvals, signatures, obligations, and renewal dates in one controlled workspace.
Create visibility into confidentiality periods, return or destruction deadlines, representative requirements, and related contract dependencies.
Preserve searchable records and audit trails that help legal and business teams demonstrate consistent review and administration.
Want to see how contract management software can simplify your legal workflows? Check out Volody's CLM Software.
FAQ
Are NDAs enforceable?
NDAs are generally enforceable when they clearly define duties and protected information. Enforceability also depends on applicable law, proportionality, and the facts surrounding disclosure. Courts may question vague, excessive, or conflicting terms. Legal review helps test the NDA against local rules, business needs, and related agreements.
What is the difference between a confidentiality agreement and an NDA?
Most businesses use “confidentiality agreement” and “NDA” for the same contract. Both limit the use or disclosure of specified confidential information. They may also cover representatives, exclusions, duration, remedies, and governing law. The title matters less than the wording and duties created.
How do you tailor an NDA to your business?
Start by identifying the deal, parties, information, purpose, threats, and likely harm. Then customize definitions, exclusions, access rules, duration, destruction steps, remedies, and ownership terms. Match the NDA to actual security practices and related contracts. Counsel should review unusual, regulated, cross-border, or high-value arrangements.
Should an NDA be mutual or unilateral?
A unilateral NDA protects information shared by one party. It often suits employees, contractors, vendors, and potential investors. A mutual NDA protects information shared by both parties. It can suit partnerships, joint ventures, and acquisition talks where both sides face disclosure risks.
What should an NDA say about compelled disclosure?
An NDA should address disclosures required by law, regulation, subpoena, or court order. It should require prompt notice when law permits that notice. The receiving party should disclose only the required information. It should also support efforts to obtain protective treatment when practical. Finalize these provisions with counsel and implement the required controls before sharing sensitive information.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.


" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)