
The 2026 eMudhra security incident exposed weaknesses in private keys used by eight intermediate certificate authorities linked to its global website-security business. The flaw triggered emergency action from major browser vendors and raised concerns about digital trust and enterprise security.
While eMudhra has stated that its Indian Digital Signature Certificate (DSC) and eSign services are unaffected, the incident highlights the need to secure every layer of digital infrastructure.
For businesses signing contracts, supplier agreements and financial documents electronically, this is a reminder to verify signatures, protect documents and maintain reliable audit trails.
What Is the eMudhra Incident?
In October 2026, a security researcher discovered a cryptographic flaw affecting eight intermediate certificate authorities linked to eMudhra’s global Transport Layer Security (TLS) certificate business.
According to CERT-In’s advisory, the private keys were generated with insufficient randomness, making them vulnerable to rapid recovery from their corresponding public keys.
The flaw was serious because certificate authorities help browsers verify website identities. If attackers obtain these private keys, they may be able to create fraudulent certificates that make malicious websites appear trustworthy, undermining internet security.
Google, Mozilla, Apple and Microsoft were involved in trust-related responses, with Google and Mozilla blocking the affected certificate authorities and broader remediation efforts following.
However, the impact is specific. eMudhra has stated that its Indian Digital Signature Certificate (DSC) and eSign services are unaffected. The incident concerns its international TLS certificate business, not evidence that all eMudhra products or electronic signatures have been compromised.
What Exactly Went Wrong?
How Digital Certificates Establish Trust
When users visit an HTTPS website, their browsers use Transport Layer Security (TLS) certificates to verify the website’s identity and establish a secure connection.
Trust follows a chain:
Root Certificate Authority: Acts as the primary trust anchor.
Intermediate Certificate Authority: Issues certificates under delegated authority.
Website Certificate: Helps verify the website’s identity.
Browser or Application: Checks the certificate chain before trusting the connection.
The private keys used by certificate authorities must remain secure. If an intermediate authority’s private key is exposed, attackers may be able to create fraudulent certificates within its permitted scope.
The Cryptographic Flaw
According to CERT-In, the affected certificates used P-384 elliptic-curve cryptography, but their private keys were generated with insufficient randomness.
Instead of being unpredictable, some keys had extremely small values that could be recovered by testing a limited number of possibilities.
The problem was not the P-384 algorithm itself, but how the keys were generated. Even strong cryptography can fail when its implementation produces predictable secrets.
How the Mistake Happened
In its incident statement, eMudhra attributed the issue to a key-generation process conducted in April 2025.
The company reported that a wrap/unwrap step generated weak keys alongside the intended strong keys. The weaker keys were then selected and used in the affected certificates.
This highlights a critical security lesson: generating keys is not enough. Organizations must verify their strength, ensure the correct keys are linked to the right certificates, and independently validate critical cryptographic processes.
Why the Discovery Was Alarming
The weak keys could reportedly be recovered with minimal computational effort, potentially making fraudulent certificate creation possible within the affected authorities’ permitted scope.
The weakness may have existed from the time the flawed certificates were created, well before its discovery in October 2026.
Related Article: What is eSign (eSignature)? How to E-Sign documents online?
Why Were Eight Intermediate Certificates So Important?
The risk came from the authority these certificates held. Unlike a certificate tied to one website, an intermediate certificate authority can issue certificates for multiple websites or entities.
If attackers recovered the affected private keys, potential risks included:
Website Impersonation: Creating fraudulent certificates to make malicious websites appear legitimate.
Man-in-the-Middle Attacks: Impersonating servers and potentially intercepting communications if attackers could also access network traffic.
Credential Theft: Stealing login details and session information through convincing fake websites.
Financial Fraud: Targeting banking portals, payment services and supplier platforms.
Software Trust Abuse: Exploiting affected code-signing authorities to make malicious software appear to come from a trusted publisher.
These are potential consequences of the vulnerability, not confirmation that all these attacks occurred.
Timeline: How the eMudhra Incident Unfolded
The following timeline summarizes publicly reported developments as of 22 October 2026.
April 2025 - Weak keys generated: A flaw in eMudhra’s key-generation process produced weak private keys that were used in affected certificates.
Mid-2025 - Certificates enter trust stores: The affected public-trust infrastructure was included in browser trust lists.
17 October 2026 - Flaw reported: Mozilla and Google received reports about the compromised private keys.
17 October 2026 - Browser protections begin: Google blocked affected TLS certificate authorities in Chrome, while Mozilla blocked affected certificates in Firefox.
18–19 October 2026 - Certificates revoked: eMudhra reported revoking all eight affected intermediate certificates and coordinating with trust-store operators.
19–20 October 2026 - Wider response: Google, Mozilla, Apple and other industry participants took or announced measures to limit trust in the affected certificates. Cloudflare also reported protective measures.
21 October 2026 - CERT-In advisory: India’s cybersecurity agency issued an advisory outlining the incident, its risks and recommended mitigations. The Ministry of Electronics and Information Technology also acknowledged the incident and announced an investigation.
27 October 2026 - Further Chrome action planned: Google announced the planned removal of the emSign ECC Root CA - G3 from the Chrome Root Store. As of 22 October, this action was still pending.
How Serious Was the Flaw?
The incident should be assessed across three areas: technical severity, confirmed exploitation and business impact.
Technical Severity: Critical
The flaw made private keys belonging to trusted certificate authorities easy to recover. These keys help establish trust between browsers and websites.
If attackers obtained and used them while the relevant certificates remained trusted, they could potentially impersonate websites, intercept communications or steal credentials. CERT-In identified these risks in its advisory.
Confirmed Exploitation: Not Established
A critical vulnerability does not automatically mean an attack occurred.
eMudhra stated that the affected intermediate authorities had not issued end-entity certificates, its infrastructure had not been compromised, and no data breach had occurred. Google also reported no Certificate Transparency records of TLS certificates chaining to the six affected TLS intermediates before its blocking action.
As of 22 October 2026, the cited public disclosures do not establish confirmed malicious exploitation of the affected keys.
Business Impact: Potentially High
The consequences extend beyond direct security threats. Blocking or distrusting certificates can disrupt legitimate websites, applications and integrations that depend on the affected trust infrastructure.
Businesses therefore face two main risks:
Security risk: Potential impersonation, credential theft and interception of communications.
Operational risk: Service disruptions, certificate replacements and remediation across browsers, systems and business applications.
How Is the eMudhra Incident Affecting Organizations Worldwide?
The impact depends on whether an organization uses the affected certificate infrastructure directly or relies on software and services that depend on it. The incident does not establish that all eMudhra customers are affected or that a global data breach occurred.
Websites and Customer-Facing Applications
Organizations using affected certificate chains may need to replace certificates and test their systems. Otherwise, browsers or applications may reject connections, disrupting customer portals, payments, onboarding and supplier services.
Banking and Financial Services
Certificate failures can increase impersonation risks and disrupt financial services. Banks and payment providers should verify their certificate dependencies, replace affected certificates where necessary, and review security and compliance controls. The incident does not itself prove that banking systems or customer data were compromised.
Enterprise Software and Cloud Services
CRM, HR, procurement, document management and other business applications may use separate certificate stores that do not update automatically. Updating browsers alone may therefore be insufficient; organizations must also check APIs, integrations, legacy applications and connected devices.
Software and Technology Providers
Vendors should review affected certificate chains, replace compromised certificates where necessary, and verify their software-signing and distribution processes. They should also ensure customers recognize updated trust relationships.
Legal, Procurement and Finance Teams
The incident does not establish that electronic signatures have been compromised. However, it highlights the importance of reliable signing and verification processes.
Organizations should maintain evidence of:
Signer identity: Who signed and how they were authenticated.
Document integrity: Which version was signed and whether it changed afterward.
Signing history: When actions occurred and who performed them.
Audit evidence: Records needed to verify the transaction and meet applicable legal requirements.
Related Article: Electronic signature Software | Top 7 eSign tools in 2024
What Should Organizations Do Immediately?
Organizations should follow CERT-In’s advisory and review their certificate dependencies without making unnecessary changes to unrelated digital-signature systems.
1. Identify Affected Systems
Check websites, APIs, servers, applications, network devices and custom software for dependencies on affected certificate chains, including application-specific trust stores.
2. Update Trust Stores
Apply relevant browser, operating-system and vendor security updates. Verify that affected certificates are rejected where required, and never disable certificate validation to restore connectivity.
3. Replace Affected Certificates
Obtain replacement certificates from a trusted, unaffected certificate authority where necessary. Test them before deploying changes to production systems.
4. Monitor Certificate Activity
Use Certificate Transparency monitoring and security alerts to identify unexpected certificates issued for your domains. Review certificate validity, issuers and revocation status.
5. Check Software-Signing Dependencies
Review affected code-signing certificates, verify software signatures and follow vendor guidance for replacing certificates or validating distributed software.
6. Review Third-Party Providers
Ask suppliers about their certificate dependencies, key-management practices, incident response and remediation plans. Ensure contracts support timely security notifications and remediation.
7. Test Business Continuity
Confirm that critical services continue working after certificate and trust-store changes. Test integrations, automated processes, mobile applications and legacy systems—not just websites.
Related Article: What is an E-Signature? A Comprehensive Guide to eSign
How Volody Sign Helps Enterprises Strengthen Digital Signing
The eMudhra incident highlights the importance of secure, traceable and well-managed digital signing. Volody e-Sign supports enterprise contract execution, but its security should be assessed based on its specific controls and architecture—not assumed to be immune to vulnerabilities.
Reliable Audit Trails
Volody supports signing records that can include signer details, timestamps, IP addresses, authentication methods and document-integrity checks, depending on the workflow. These records help teams verify who signed, when they signed and which document was executed.
Encryption and Document Protection
Volody describes security controls including encryption in transit and at rest, role-based access and audit trails. Enterprises should verify the encryption design, key-management practices, access permissions and data-protection controls applicable to their deployment.
Controlled Signing Workflows
Configurable approval rules, sequential or parallel signing and automated reminders help ensure agreements reach the right people in the correct order. This improves accountability and reduces delays across legal, procurement, finance, HR and sales.
AI-Powered Contract Management
Beyond signing, Volody offers capabilities such as AI-assisted contract review, clause analysis, drafting support, document search, obligation tracking and renewal reminders. These help teams identify risks before execution and monitor commitments afterward.
AI supports contract review and management; it does not replace cryptographic validation, security controls or legal judgment.
A Connected Contract Lifecycle
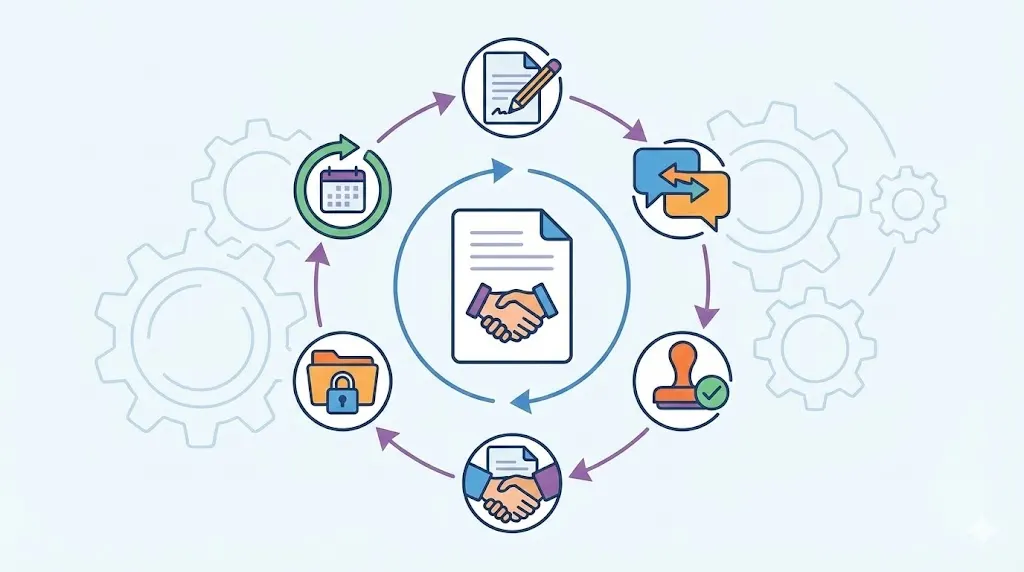
Connecting review, approval, signing, storage and post-signature tracking reduces manual handoffs and keeps contract information organized throughout its lifecycle.
About the Company
Volody AI CLM is an Agentic AI-powered Contract Lifecycle Management platform designed to eliminate manual contracting tasks, automate complex workflows, and deliver actionable insights. As a one-stop shop for all contract activities, it covers drafting, collaboration, negotiation, approvals, e-signature, compliance tracking, and renewals. Built with enterprise-grade security and no-code configuration, it meets the needs of the most complex global organizations. Volody AI CLM also includes AI-driven contract review and risk analysis, helping teams detect issues early and optimize terms. Trusted by Fortune 500 companies, high-growth startups, and government entities, it transforms contracts into strategic, data-driven business assets.
" height="216.72211px" id="FYO0bO80Y" transform="translate(3 6.105)" width="206.073px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.044 89.731 216.044 110.845 C 216.044 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.533 125.334 172.533 110.845 C 172.533 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.109 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.109 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="aa1McFcE9" transform="translate(227.183 3)" width="216.04399999999998px"/><path d="M 42.302 182.257 L 111.799 182.257 L 111.799 216.722 L 0 216.722 L 0 0 L 42.302 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="yRq4AnrsX" transform="translate(477.721 6.105)" width="111.79899999999998px"/><path d="M 108.174 222 C 88.432 222 70.303 217.239 53.785 207.717 C 37.267 198.196 24.173 185.052 14.504 168.285 C 4.835 151.312 0 132.165 0 110.845 C 0 89.731 4.835 70.792 14.504 54.025 C 24.173 37.052 37.267 23.804 53.785 14.282 C 70.303 4.761 88.432 0 108.174 0 C 128.116 0 146.246 4.761 162.562 14.282 C 179.08 23.804 192.073 37.052 201.541 54.025 C 211.21 70.792 216.045 89.731 216.045 110.845 C 216.045 132.165 211.21 151.312 201.541 168.285 C 192.073 185.052 179.08 198.196 162.562 207.717 C 146.044 217.239 127.915 222 108.174 222 Z M 108.174 183.189 C 120.864 183.189 132.044 180.291 141.713 174.495 C 151.382 168.492 158.936 160.006 164.375 149.035 C 169.814 138.064 172.534 125.334 172.534 110.845 C 172.534 96.355 169.814 83.729 164.375 72.965 C 158.936 61.994 151.382 53.611 141.713 47.815 C 132.044 42.02 120.864 39.122 108.174 39.122 C 95.483 39.122 84.202 42.02 74.332 47.815 C 64.663 53.611 57.108 61.994 51.67 72.965 C 46.231 83.729 43.511 96.355 43.511 110.845 C 43.511 125.334 46.231 138.064 51.67 149.035 C 57.108 160.006 64.663 168.492 74.332 174.495 C 84.202 180.291 95.483 183.189 108.174 183.189 Z" fill="rgba(255, 255, 255, 0.12)" height="222px" id="mo8HQspQ0" transform="translate(609.155 3)" width="216.04500000000007px"/><path d="M 73.727 0 C 95.885 0 115.324 4.45 132.044 13.351 C 148.967 22.252 161.957 34.982 171.027 51.541 C 180.287 67.894 184.917 86.937 184.917 108.671 C 184.917 130.405 180.287 149.449 171.027 165.801 C 161.957 181.947 148.967 194.47 132.044 203.371 C 115.324 212.271 95.885 216.722 73.727 216.722 L 0 216.722 L 0 0 Z M 72.216 179.773 C 94.374 179.773 111.497 173.564 123.583 161.144 C 135.669 148.724 141.713 131.233 141.713 108.671 C 141.713 86.109 135.669 68.515 123.583 55.888 C 111.497 43.055 94.374 36.638 72.216 36.638 L 42.302 36.638 L 42.302 179.773 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="I3iXX5Hi_" transform="translate(859.693 6.105)" width="184.91699999999992px"/><path d="M 185.22 0 L 113.91 141.273 L 113.91 216.722 L 71.61 216.722 L 71.61 141.273 L 0 0 L 47.74 0 L 93.06 99.046 L 138.08 0 Z" fill="rgba(255, 255, 255, 0.12)" height="216.72211px" id="nzHyWC0_d" transform="translate(1061.78 6.105)" width="185.22000000000003px"/></svg>)